• rss_feed
    add Follow

    Torrent Freak

    people 423 subscribers • TorrentFreak is a publication dedicated to bringing the latest news about copyright, privacy, and everything related to filesharing.

    • chevron_right

      Pirate Site Movix’s Source Code Survives Four Rounds of GitHub Takedowns

      news.movim.eu / TorrentFreak • 8:04 • 3 minutes
    movix logoIn March, a Paris court ordered French Internet providers Orange, SFR, Free and Bouygues Telecom to block Movix, together with 21 other pirate sites.

    Like many pirate sites, the streaming portal simply moved on to new domain names. However, Movix also stands out in another way. The code that powers the site is shared openly on GitHub, for anyone to copy and use.

    The repository includes the site’s frontend and backend, as well as a browser extension and mobile apps. The README presents Movix as France’s first open source streaming site with an AI twist, adding that it was entirely vibe-coded.

    Takedown and Repeat

    The shared code didn’t go unnoticed, of course. ALPA, the French anti-piracy group whose members include the local arms of major Hollywood studios, the MPA and music rights group SACEM, has been sending takedown notices to GitHub over the Movix code since March.

    The first two notices were sent in March and April, targeting Movix repositories uploaded by the same GitHub account. GitHub blocked both repositories at the time. In the second notice ALPA also asked the platform to ban the uploader, but the account is still active today.

    While the repositories were taken offline, the source code soon resurfaced. A new GitHub account was created two weeks after the April takedown, and archived copies show that it hosted a fresh copy of the code by early May. Late June, the repository had 94 stars and 21 forks.

    ALPA eventually went after that repository too, sending a new takedown request in September, and GitHub blocked it the next day. That still left the forks online, however, which ALPA eventually targeted last week.

    “We are now targeting forks which are exact copies,” ALPA writes in its notice, which lists 38 forks. The forks we checked were blocked by GitHub a day later.
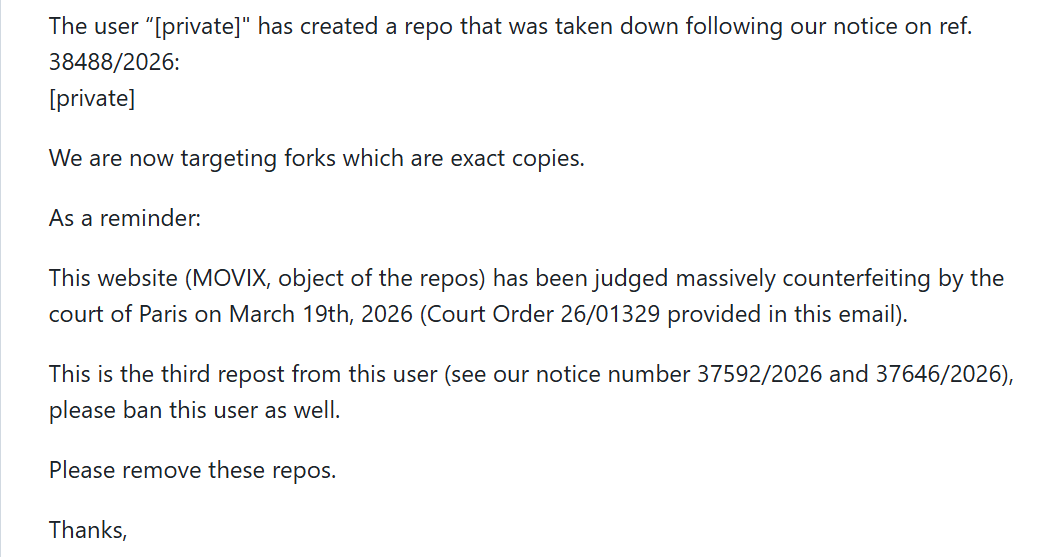
    ALPA’s notice

    ban this user

    The notice doesn’t mention any specific movies or TV shows either. ALPA writes that its members own the rights to the titles “listed below”, but there are none mentioned.

    ALPA also repeats its request to ban the uploader of the September repository, linking it to the March and April copies. Its September notice made the same claim about that second GitHub account, using the exact same words.

    “This is the third repost from this user […] please ban this user as well,” ALPA’s latest notice reads.

    ALPA’s Movix takedown notices
    Notice Target Blocked by GitHub
    March 26 First Movix repository March 26
    April 14 Second repository, same account (ban requested) April 14
    September 22 New repository, second account September 23
    November 12 38 forks November 13*

    * Date for the forks we checked

    A Paris Court Order

    ALPA’s recent notices point to the blocking order from the Paris Judicial Court. This was issued following a request from several French film industry groups, ordering Internet providers to block 22 pirate sites for 18 months.

    This order also shows how popular Movix was. According to the evidence presented to the court, the site offered 7,236 movies and 2,956 series without permission.

    The same evidence, provided by ALPA’s sworn agents, shows that Movix drew more than 387,000 unique French visitors in a single month. That’s more than any of the other 21 sites in that blocking order.
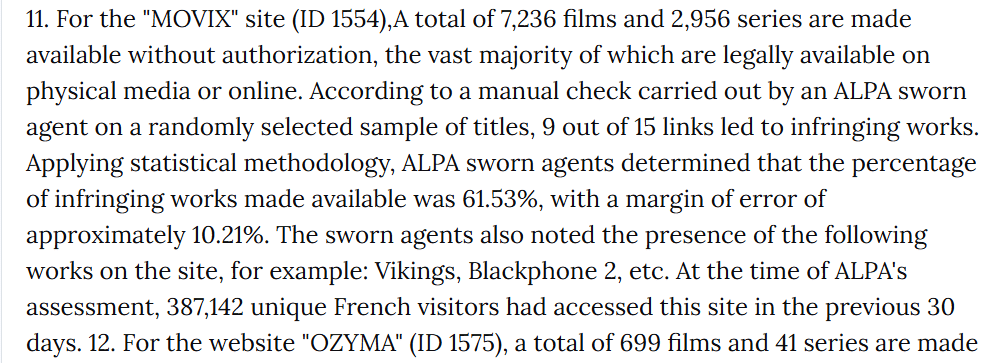
    Movix in the court order (translated)

    movix order

    The Code Lives On

    ALPA’s Github takedowns removed the targeted repositories, but now the code itself is leading a life of its own. A fresh copy is still online today, under yet another new GitHub account.

    Data from GitHub shows that both the GitHub account and the repository were created on September 24, less than a day after GitHub blocked the previous version.

    According to its commit messages, the repository mirrors the full Movix code excluding some private files. The most recent sync was on November 15, which is three days after ALPA’s latest notice. These updates are credited to the GitHub user that ALPA asked GitHub to ban in April.

    In addition to the code, there is no shortage of full streaming sites using the Movix brand today. Whether ALPA will target these and the new GitHub copy, which already has 21 forks of its own, has yet to be seen.

    —

    ALPA’s latest takedown notice is available on GitHub. The Paris court order can be found here (in French).

    From: TF, for the latest news on copyright battles, piracy and more.
    • chevron_right

      DISH Wants $21m From Pirate IPTV Operators Who Ignored Its Lawsuit

      news.movim.eu / TorrentFreak • 1 day ago • 3 minutes

    In February, DISH Network took the people allegedly behind DMTN IPTV to court in New York.

    The pay-TV provider accused Moroccan resident Idriss Elkasmi of running the service, which was also sold as Idriss Premium TV and Manx TV. According to the complaint, payments were processed through an online store called Genuine Leather, and Elkasmi swapped his Facebook photo for one of Breaking Bad creator Vince Gilligan.

    A month later, DISH amended its complaint, adding Tunisian resident Makrem Salem as a second alleged operator. In its latest filings, DISH adds that a company that previously hosted the service’s server identified Salem as the owner of the account used to manage it.

    Elkasmi, for his part, pushed back. In an email to DISH’s counsel, he claimed to be “only a freelance website designer,” the amended complaint notes.

    Served by Email

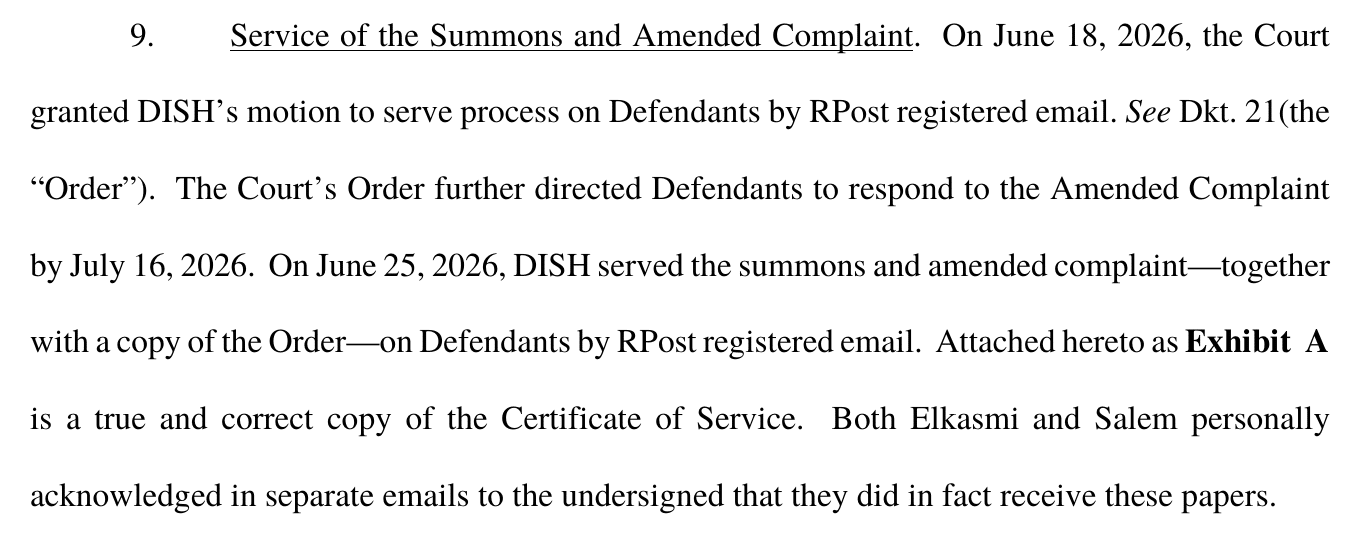
    In June, the court allowed DISH to serve the summons and amended complaint by registered email. The order also gave the defendants until July 16 to respond.

    DISH sent the papers on June 25. Elkasmi and Salem then both confirmed in separate emails to DISH’s lawyer that they had received them.

    Acknowledged

    ack

    However, the defendants did not formally respond to the complaint. As a result, the Clerk of Court certified their default in August.

    Last week, DISH asked the court to turn this into a default judgment. According to the pay-TV provider, the defendants simply continued operating after they were served.

    “Defendants’ infringement has continued unabated, even after they each personally acknowledged to DISH that they had received the Amended Complaint in this lawsuit,” DISH writes.

    Still Selling

    The operators of the IPTV service did make some changes. According to DISH’s motion, they briefly disabled their website after the lawsuit was filed, to then launch a new one with new features. They also released a new Android app.

    Gregory Duval, CEO of NagraStar, which investigated the service for DISH, adds that the service was still streaming the channels at issue in the United States last week.

    “They seek to evade enforcement of U.S. copyright laws by working from secret locations in Morocco and Tunisia, using an array of constantly changing servers, and operating through fictitious shell companies with names like ‘Genuine Leather’ and ‘VPS Designs,'” the motion reads.

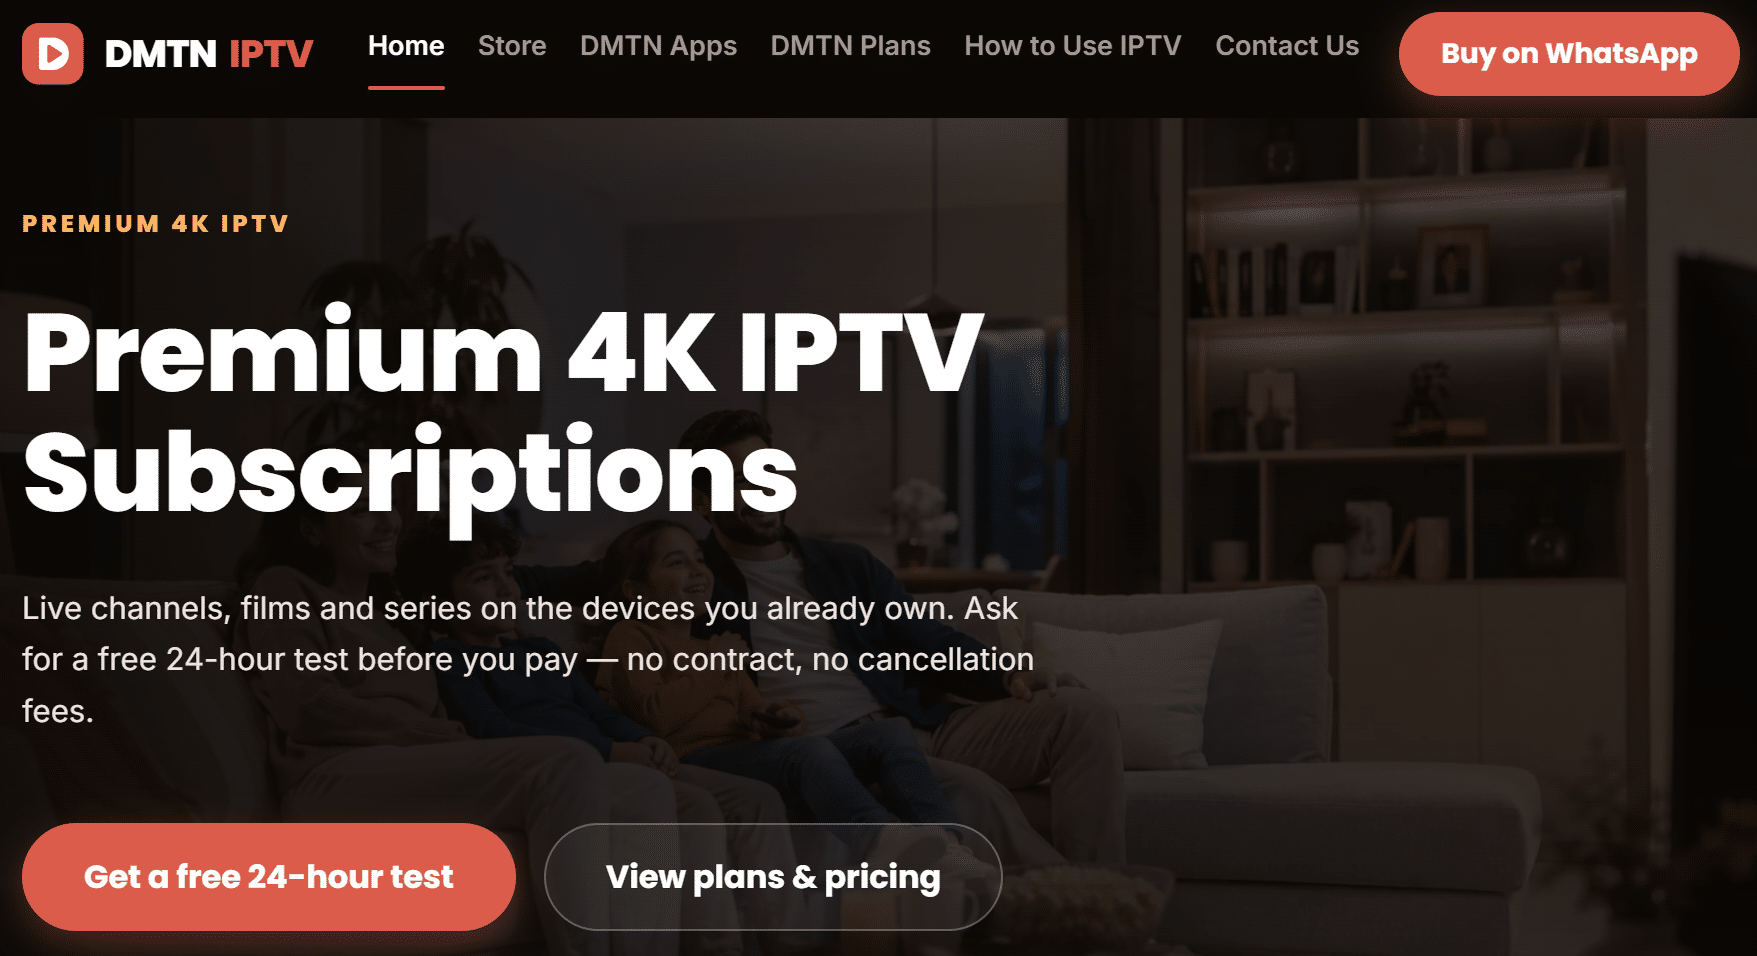
    The pirate IPTV service is also still openly for sale. When we checked this week, the DMTN IPTV website offered a 12-month subscription for €70, discounted from €85, and promised “Instant WhatsApp activation.”

    DMTN IPTV today

    DMTN today

    $21 Million and a Broad Injunction

    In its motion, DISH asks the court to award the maximum statutory damages of $150,000 for each of the 141 registered works listed in the complaint. That adds up to $21.15 million, with both defendants liable for the full amount.

    DISH also requests a permanent injunction. This would bar the defendants from offering DMTN IPTV, or any comparable service that carries DISH’s programming, “wherever they may be found,” and it would also apply to anyone who receives notice of the order.

    To shut the service down, DISH lists several third-party companies that should be bound to the injunction as well. These include hosting companies and domain registrars, but also WhatsApp, Gmail and live chat provider tawk.to, which the service uses to communicate with customers.

    Third parties named in the proposed injunction
    Company Role Target
    IPv4 Superhub (Hong Kong) Registrant of server IPs 45.155.90.76, 45.155.90.16
    ISTQSERVERS Upstream network provider 45.155.90.76, 45.155.90.16
    GoDaddy Registrar, content server dmtn-tv.com
    OVH Registrar and DNS, content server one-x.best, smart-tv.cc
    Hostinger Web host, website dmtn8k.com
    Key-Systems Registrar, website dmtn8k.com
    Veeble Hosting Web host, websites iptv-subscription.com, smart-iptv.info
    PDR Ltd. Registrar, websites iptv-subscription.com, smart-iptv.info
    WhatsApp (Meta) Customer communication Two phone numbers
    Google (Gmail) Contact email dmtniptvserver@gmail.com
    tawk.to Live chat iptv-subscription.com

    The domain registrars, including GoDaddy and OVH, would have to disable the listed domains and transfer them to DISH at its direction. The same applies to “any other domain names used (now or in the future)” in connection with the service.

    For now, DMTN IPTV continues to sell its subscriptions as usual. Whether the companies named in the proposed injunction will have to cut off their services depends on the court’s decision.

    —

    A copy of DISH’s memorandum of law in support of the motion for default judgment is available here (pdf). The declaration of Adam Rich and the proposed default judgment and permanent injunction can be found here (pdf).

    From: TF, for the latest news on copyright battles, piracy and more.

    • chevron_right

      Alleged Operator of Pirate Site Movie2K Could Walk Free as Bitcoin Billionaire

      news.movim.eu / TorrentFreak • 2 days ago • 3 minutes

    movie2kMore than a decade ago, Movie2K was one of the most visited websites in Germany, beating Twitter and Amazon.
    The site shut down in 2013. By then, its operators had allegedly converted much of their advertising income into bitcoin. This was an early bet that eventually turned into billions.

    In January 2024, German authorities secured around 50,000 bitcoin, which the alleged operator handed over after his arrest in Spain the year before. The state of Saxony moved these coins to exchanges that summer and eventually sold them for roughly $2.9 billion (€2.64 billion).

    That wasn’t the first haul. In 2020, the authorities had already seized 2,700 bitcoin in the same investigation.

    The proceeds of the 2024 sale are now held by the state’s judicial cash office. However, according to the court, the money still belongs to the defendant until there’s a final verdict.

    Copyright Charges Expired

    The criminal trial against the alleged operator and a co-defendant started at the Leipzig Regional Court in February. Prosecutors initially accused the main defendant of commercial copyright infringement in roughly 220,000 cases.

    Movie2K.to

    Movie2K.to

    The court concluded that these copyright offenses were time-barred, so they are no longer part of the case. The main defendant now stands trial for, among other things, commercial money laundering in more than 100 cases. The co-defendant faces dozens of money laundering counts and tax evasion.

    The piracy accusations still matter though. According to the indictment, the operators made millions from advertising deals on the site and used that money to buy bitcoin.

    From Suspended Sentence to a Dismissal

    In April, presiding judge Karsten Nickel already floated a potential deal, MDR and German news site Tarnkappe reported at the time. If the main defendant confessed, he could get a prison sentence of one to one and a half years, suspended on probation.

    That’s far below the maximum sentence of 13 years mentioned in earlier media reports.

    As part of that deal, the main defendant would also have to hand over the access credentials to another 57,000 bitcoin. The defense lawyers criticized this approach as mainly “economically driven” and left open whether they would agree to such a deal.

    Talks between the court, prosecutors and the defense continued behind closed doors, and last week Judge Nickel came back with a new proposal. This time, there is no sentence on the table at all.

    New Deal

    The case against the main defendant could be dropped if he transfers 40,000 bitcoin to the authorities, a spokesperson for the Dresden General Prosecutor’s office confirmed to dpa. The court itself had not confirmed the proposal when dpa reported on it.

    The alleged operator would also have to pay roughly $42 million (€38 million) to compensate possible victims, such as rightsholders. According to Freie Presse, he would also give up his claim to the billions Saxony already raised from the earlier sale.

    Meanwhile, the co-defendant would have to hand over 600 bitcoin and $19 million (€17 million). His lawyer said she could imagine accepting that offer, while the main defendant’s lawyers are still weighing their options.

    Still a Billionaire?

    Even if the main defendant accepts the deal, he could still be left with sizable fortune. Prosecutors believe he holds roughly 56,000 bitcoin, which mean that he could keep about 16,000 coins, which is worth just over $1 billion (€945 million) at today’s rate.

    Leipziger Volkszeitung reports that the judge doubts whether all the bitcoin were obtained illegally, which complicates the case.

    At the same time, it’s not yet certain that the alleged operator actually controls all the bitcoin attributed to him, and the deal depends on that, Tarnkappe notes.

    For now, nothing is final. The defense and the prosecutors are still reviewing the proposal. The next hearing is scheduled for December 3. If all parties agree, the case could be over before Christmas.

    —

    The German-language quotes in this article were translated by TorrentFreak.

    From: TF, for the latest news on copyright battles, piracy and more.

    • chevron_right

      Reddit’s Copyright Removals Rise as Repeat Infringer Bans Drop

      news.movim.eu / TorrentFreak • 2 days ago • 2 minutes

    redditEvery day, more than 130 million users visit Reddit, sharing millions of posts and comments. Some of these include or link to copyright-infringing content.
    When rightsholders spot these, they can send a DMCA takedown notice to Reddit, which then decides whether to remove it or not. The company reports this takedown activity in its biannual transparency report, of which the latest version came out last week.

    More Removals, Fewer Takedown Notices

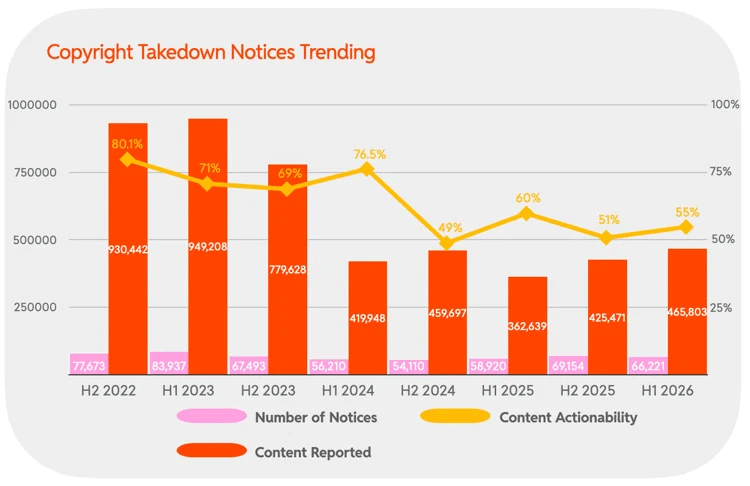
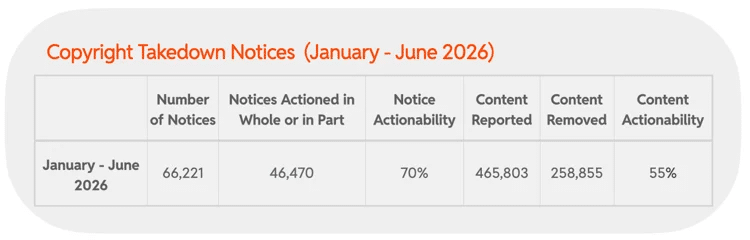
    The latest transparency report covers the first half of 2026. During this period, Reddit received 66,221 copyright takedown notices, 4% fewer than in the second half of last year.

    While there were (marginally) fewer notices, they targeted more posts, comments, and other content. In the first half of the year, rightsholders identified 465,803 pieces of content, an increase of 9% compared to the previous reporting period.

    Reddit removed 258,855 of these items. That’s 55% of all reported content, up from 51% in the second half of 2025.

    Reddit’s H1 2026 takedown overview

    Reddit's H1 2026 takedown overview

    Looking at the longer trend, we see that the number of notices and flagged posts and comments remains on a lower level than in 2022 and 2023. This, despite the fact that Reddit’s active users continued to grow.

    Copyright takedown notices trend

    Copyright takedown notices trend

    Copyright-Related Bans Plunge

    Although Reddit removed more content than it did last year, it banned fewer repeat infringers. In the first half of 2026, Reddit banned 1,266 user accounts for repeat copyright violations, which is a 21% drop compared to the six months before.

    This might in part be reversion to the mean as last year the number of user bans had nearly doubled.

    The decline is even steeper for communities. Reddit banned 118 subreddits for repeat copyright violations, down 79% from 563 in the second half of 2025. In the first half of 2025, that number was still 709.

    Reddit doesn’t explain this recent drop. However, zooming out reveals that these numbers are also far below 2022 levels. In the first half of that year alone, Reddit banned 3,859 user accounts and 1,543 subreddits for repeat infringement.

    Counter-Notices and Fair Use

    Meanwhile, Redditors are also pushing back against takedown notices more often. In the first half of this year, Reddit received 688 counter-notices, which is 60% more than in the previous period. Of these, 221 were valid, resulting in 599 pieces of content being restored. That’s a big jump compared to the second half of 2025, when just 34 of 430 counter-notices were valid.

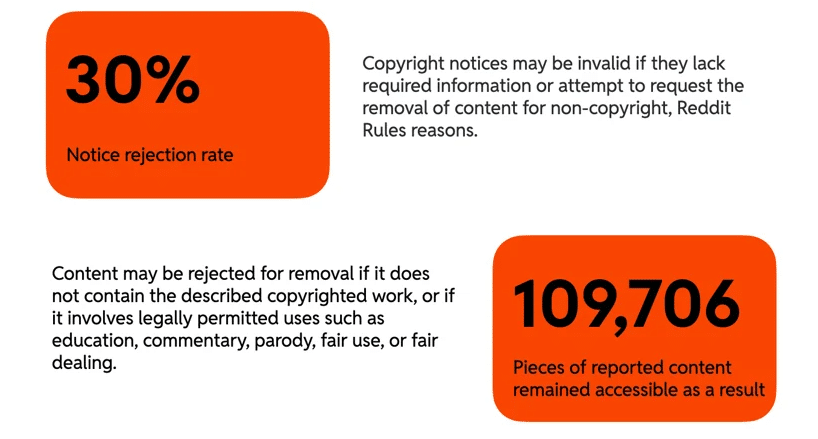
    Reddit also rejected 20,143 takedown notices outright, 30% of the total, leaving 109,706 pieces of content in place. The company explains that takedown notices can be invalid for various reasons, including when the targeted content makes fair use of a copyrighted work.

    Rejected notices

    reddit rejected

    The report highlights a few notable requests. A religious organization, for example, tried to remove two posts that reproduced the text of an internal announcement, together with extensive commentary and criticism.

    “We declined to remove the posts because they make fair use of the original work,” Reddit writes.

    Another notice came from an individual in Australia, who objected to a Reddit user’s photo of their business card. The card had allegedly been handed to the sender’s partner in a public park.

    “Because the business card (stating: “Gentleman of Leisure”) did not contain personally identifiable information or any creative elements, we declined to remove the content,” Reddit notes.

    That will be the first report to cover a full six months after the Supreme Court’s Cox ruling, which cleared the Internet provider of liability for not disconnecting repeat infringers.

    Whether this will have an impact on the repeat infringer bans has yet to be seen.

    From: TF, for the latest news on copyright battles, piracy and more.

    • chevron_right

      Game Repacker DODI Retires Ahead of Wedding, Hands Site to New Team

      news.movim.eu / TorrentFreak • 5 days ago • 3 minutes

    dodiNext to FitGirl, DODI Repacks is one of the best known names among game pirates.
    The site publishes ‘repacks’ of pirated games. These are compressed versions of cracked games, which are smaller to download and are shared through torrents and direct download links.

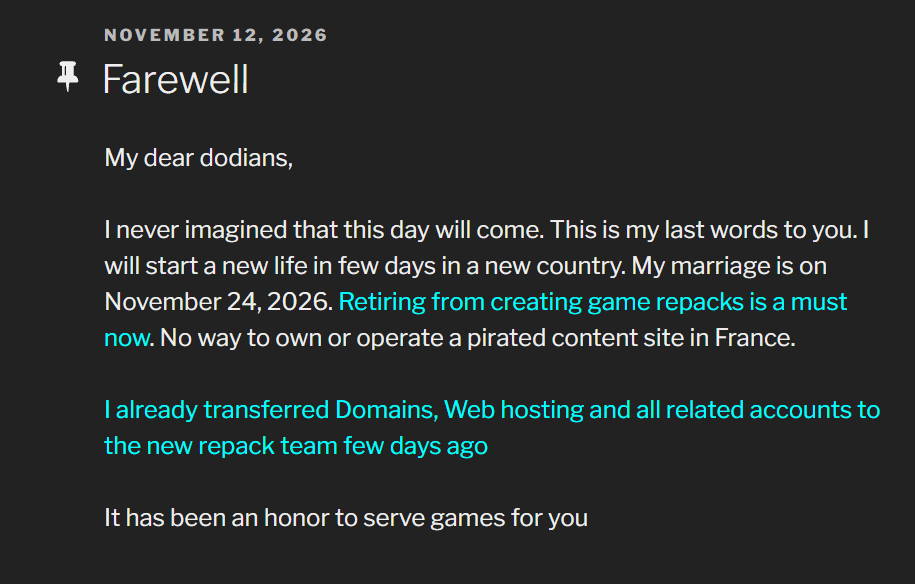
    However, yesterday the site’s operator announced that it’s time to say goodbye. In a farewell message, DODI explains that he is getting married later this month and will start a new life in a new country.

    “My marriage is on November 24, 2026. Retiring from creating game repacks is a must now. No way to own or operate a pirated content site in France,” DODI writes.

    Farewell

    Farewell

    The site isn’t going offline though. “I already transferred Domains, Web hosting and all related accounts to the new repack team few days ago,” DODI adds.

    Not a Sudden Exit

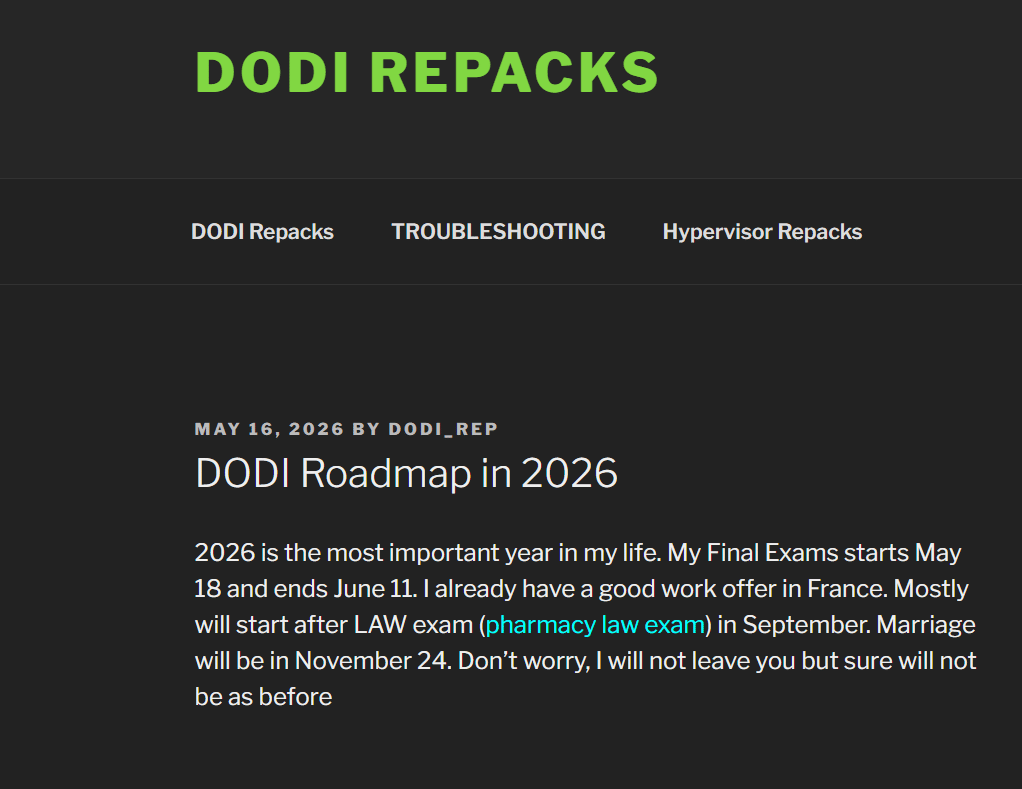
    The retirement wasn’t entirely unexpected. In May, DODI informed his followers that 2026 would be a busy year. He had final exams coming up, followed by a pharmacy law exam in September, after which he would likely start a new job in France. In addition, he was getting married in November.

    “Don’t worry, I will not leave you but sure will not be as before,” DODI wrote at the time.

    Last month, DODI revealed that the handover had already started, noting that he only created four of the more than 65 repacks that were posted in the previous six weeks. The rest came from a new team, which would also handle all future releases.

    “I will only give instructions and watch,” he wrote.

    A Notorious Target

    DODI’s exit also follows continued pressure from the game industry. In 2024, the Entertainment Software Association (ESA) added the site to its list of recommendations for the U.S. Trade Representative’s annual review of ‘notorious’ piracy markets.

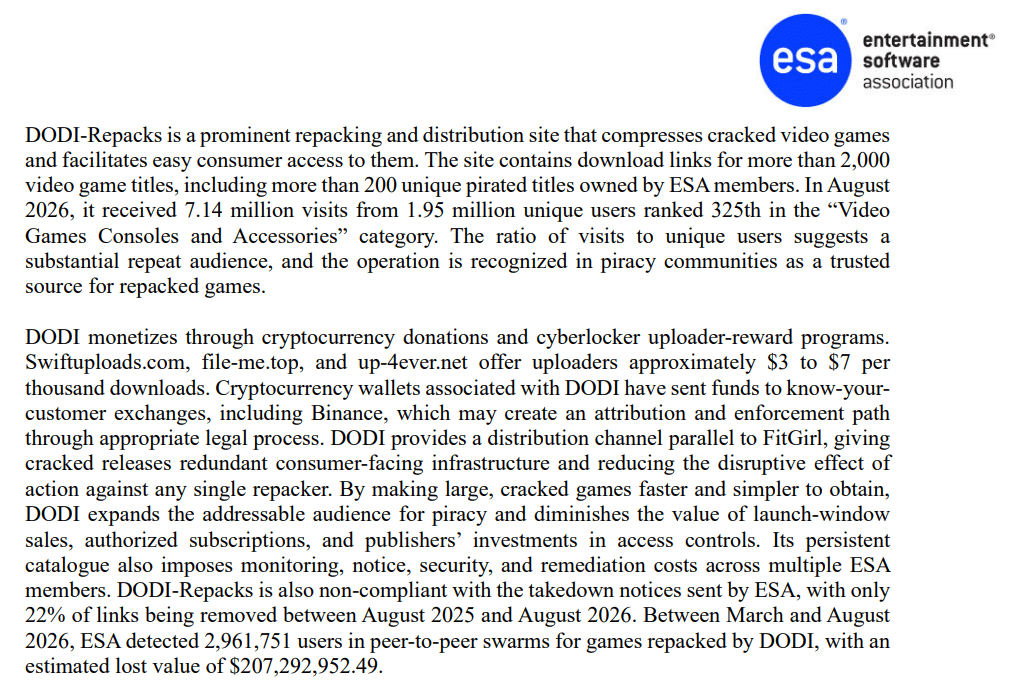
    Last month, ESA flagged the site again, reporting 7.14 million visits in August and links to more than 2,000 games. According to ESA, the site removed only 22% of the links it reported over the past year.

    ESA on DODI

    ESA on DODI

    The game industry group also looked closely at the money trail, identifying crypto payments to exchanges that check the identity of users.

    “Cryptocurrency wallets associated with DODI have sent funds to know-your-customer exchanges, including Binance, which may create an attribution and enforcement path through appropriate legal process,” ESA writes.

    Malware Concerns

    Previously, DODI’s site faced a security backlash too. In February, cybersecurity company Cyderes listed dodi-repacks.site among the indicators in its analysis of the ‘RenEngine’ malware, with a download link supposedly leading to an infected MediaFire file. The report didn’t say that DODI’s operator was involved.

    Malware concerns have also been mentioned in piracy circles. In 2025, the FMHY piracy index dropped the site and only linked to DODI’s 1337x page instead, with a warning. This year, r/Piracy’s moderators followed suit.

    “Because Dodi’s repacks themselves are still safe (even though his site is not), we have changed his listing on the megathread to send redditors to his user profile on 1337x,” the moderators wrote.

    Under New Management

    Who is behind the new repack team is not known. For now, however, it appears that new releases continue to come out under the DODI name.

    The latest repack, posted on the same day as the farewell message, credits the “Dodi Repack Team.” It’s based on a Star Wars: Galactic Racer release from ‘voices38’, another familiar piracy name that ESA nominated as a notorious piracy threat.

    —

    A copy of ESA’s submission for the 2026 Notorious Markets review is available here (pdf).

    From: TF, for the latest news on copyright battles, piracy and more.

    • chevron_right

      Copyright-Strike-for-Hire: Lawsuit Targets Service Over Fake Meta Takedowns

      news.movim.eu / TorrentFreak • 6 days ago • 4 minutes

    dogsfightEarlier this year, we reported how scammers allegedly abused Meta’s Rights Manager to claim other creators’ videos and hit their accounts with copyright strikes.
    Regular DMCA takedown notices can do similar damage. Meta’s takedown emails remind users that it terminates the accounts of repeat infringers “when appropriate,” which turns false notices into an effective weapon.

    According to a lawsuit filed in Florida federal court last week, that weapon can be hired too. This lawsuit’s backstory involves two dog book publishers and a takedown contractor who tried to play both sides.

    A Dog Eat Dog Playbook

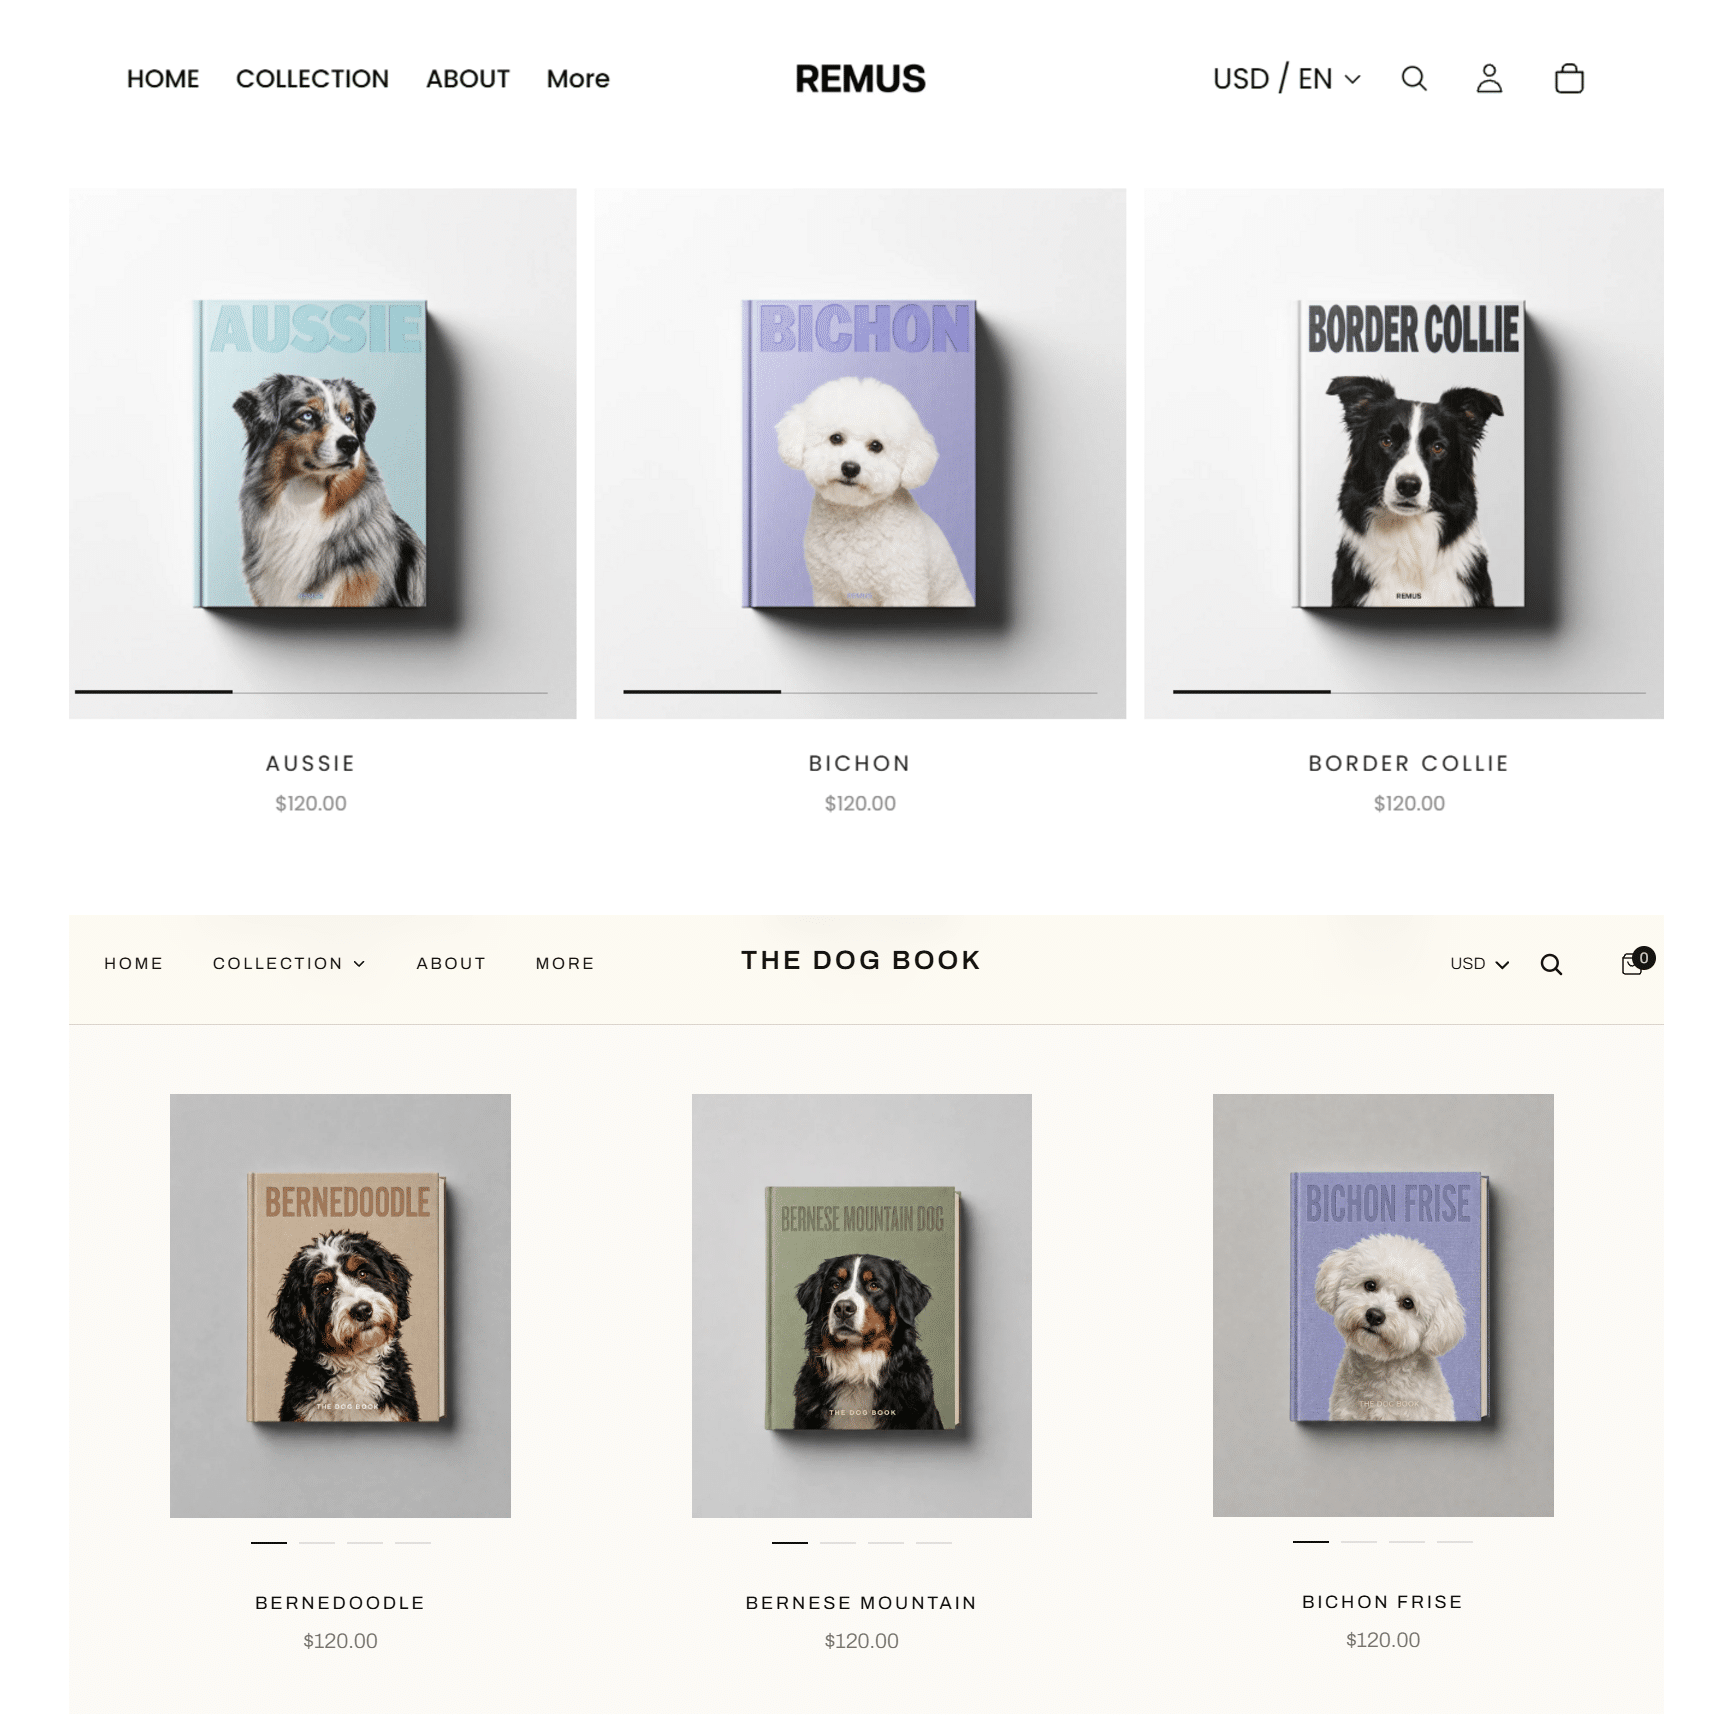
    The complaint was filed by The Everything Editions LLC, which sells photo books of various dog breeds for $120 each under the name The Dog Book.

    Rival publisher Remus Collection is one of the defendants in this case. This company also sells dog breed books for $120, and in August it accused The Dog Book of infringing its copyrights. The Dog Book disputed this and, among other things, questioned whether Remus’s own website copy was written by a human or by an AI tool.

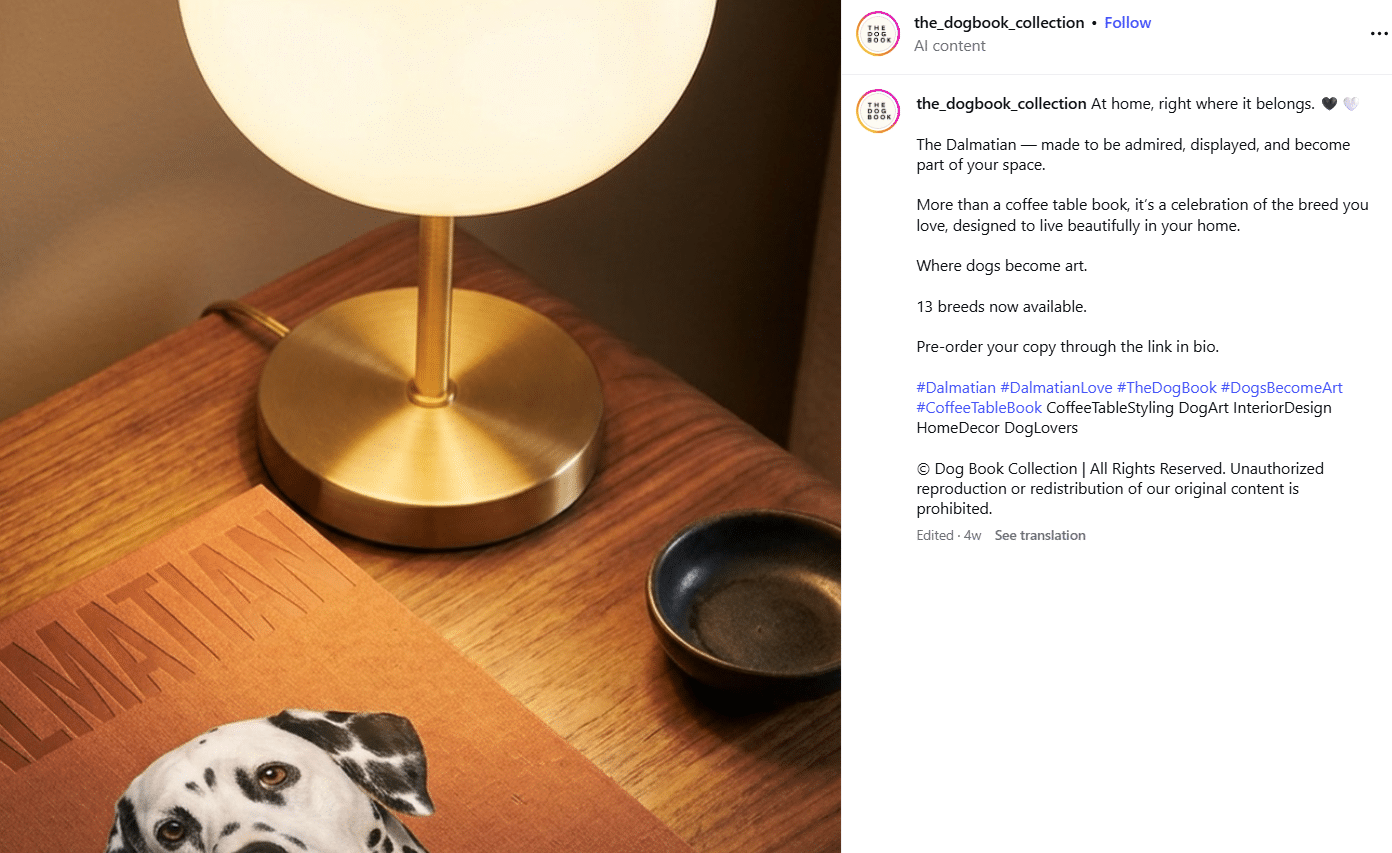
    Interestingly, The Dog Book’s own Instagram features several posts of books and images that have an ‘AI content’ label, but that’s beside the point.

    Remus (top) and The Dog Book (bottom)

    Remus and The Dog Book

    Remus never answered those questions, according to the complaint. Instead, a Remus principal and others asked their Instagram followers to report The Dog Book “for scam/fraud.” This apparently worked, as Instagram suspended The Dog Book’s account on September 7, citing its account integrity standards.

    After a cease and desist letter, Remus’s lawyer agreed in writing that Remus would stop calling The Dog Book a scam or fraud, the complaint notes. However, that didn’t end the matter, and the complaint alleges that the attack continued underground.

    Monetized Copyright Strikes

    The Dog Book opened new Instagram accounts, but these were reported and disabled too, the complaint says. The first replacement went down on September 9, a day after Remus’s lawyer agreed to stop.

    In early October, Meta received six copyright notices targeting The Dog Book’s Instagram posts. These included photos and videos of Yorkshire Terriers, Dachshunds, a Cocker Spaniel and a Jack Russell.

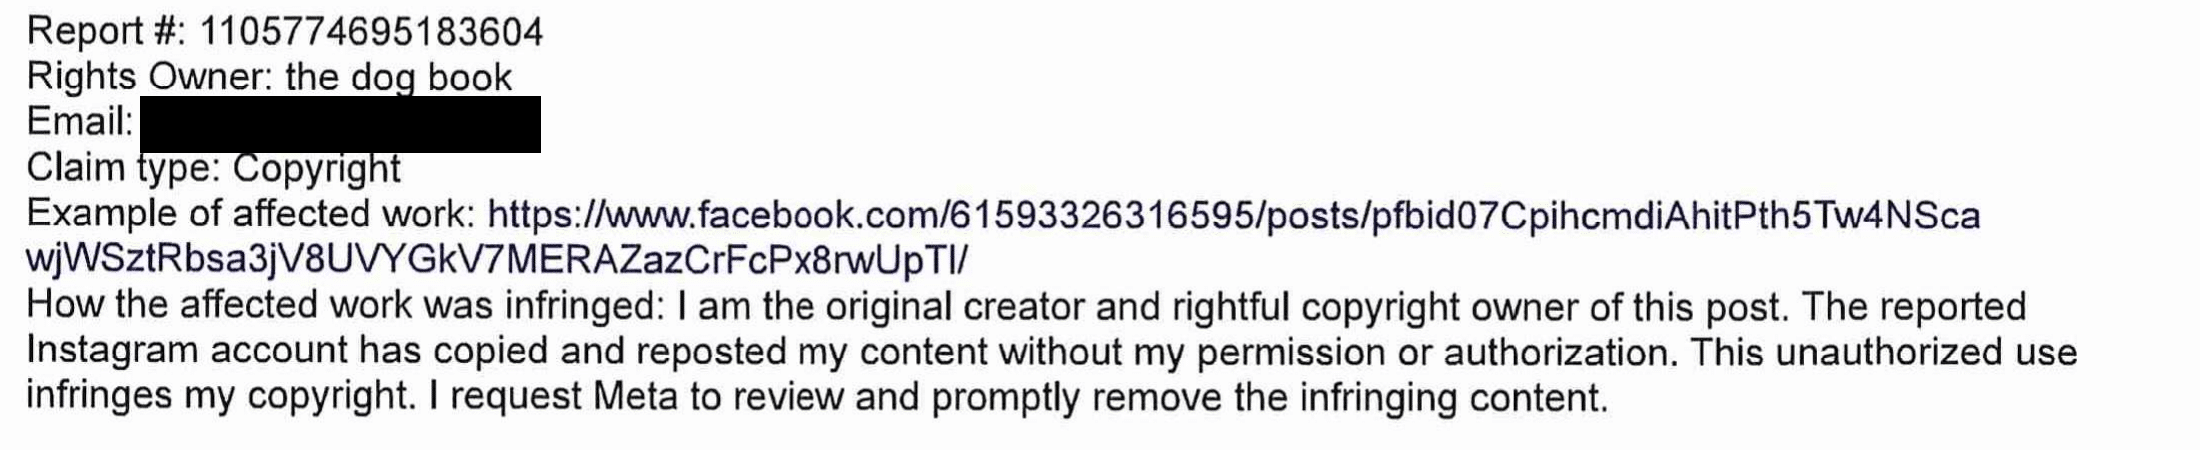
    Interestingly, these notices were filed in the name of The Dog Book itself. They all listed “The dog book” as rightsholder, while claiming to own the bookseller’s posts.

    ‘Rights Owner: the dog book’

    Rights Owner: the dog book

    Meta took action in response to these notices, adding to The Dog Book’s continued trouble. According to the complaint, the takedown actions were the work of a hired gun, who surprisingly tried to play both sides.

    Takedown Vendor Plays Both Sides

    In mid-October, a man using the name “Ashmit Ashmit” reached out to The Dog Book’s Facebook page, claiming responsibility for the copyright strikes on its accounts. He also came with a proposal.

    “One guy need to ban your fb and ig both. He his paying me 1k doller. I also strike cpr on your accounts i will take all back and i have a good plan if you agree,” he wrote.

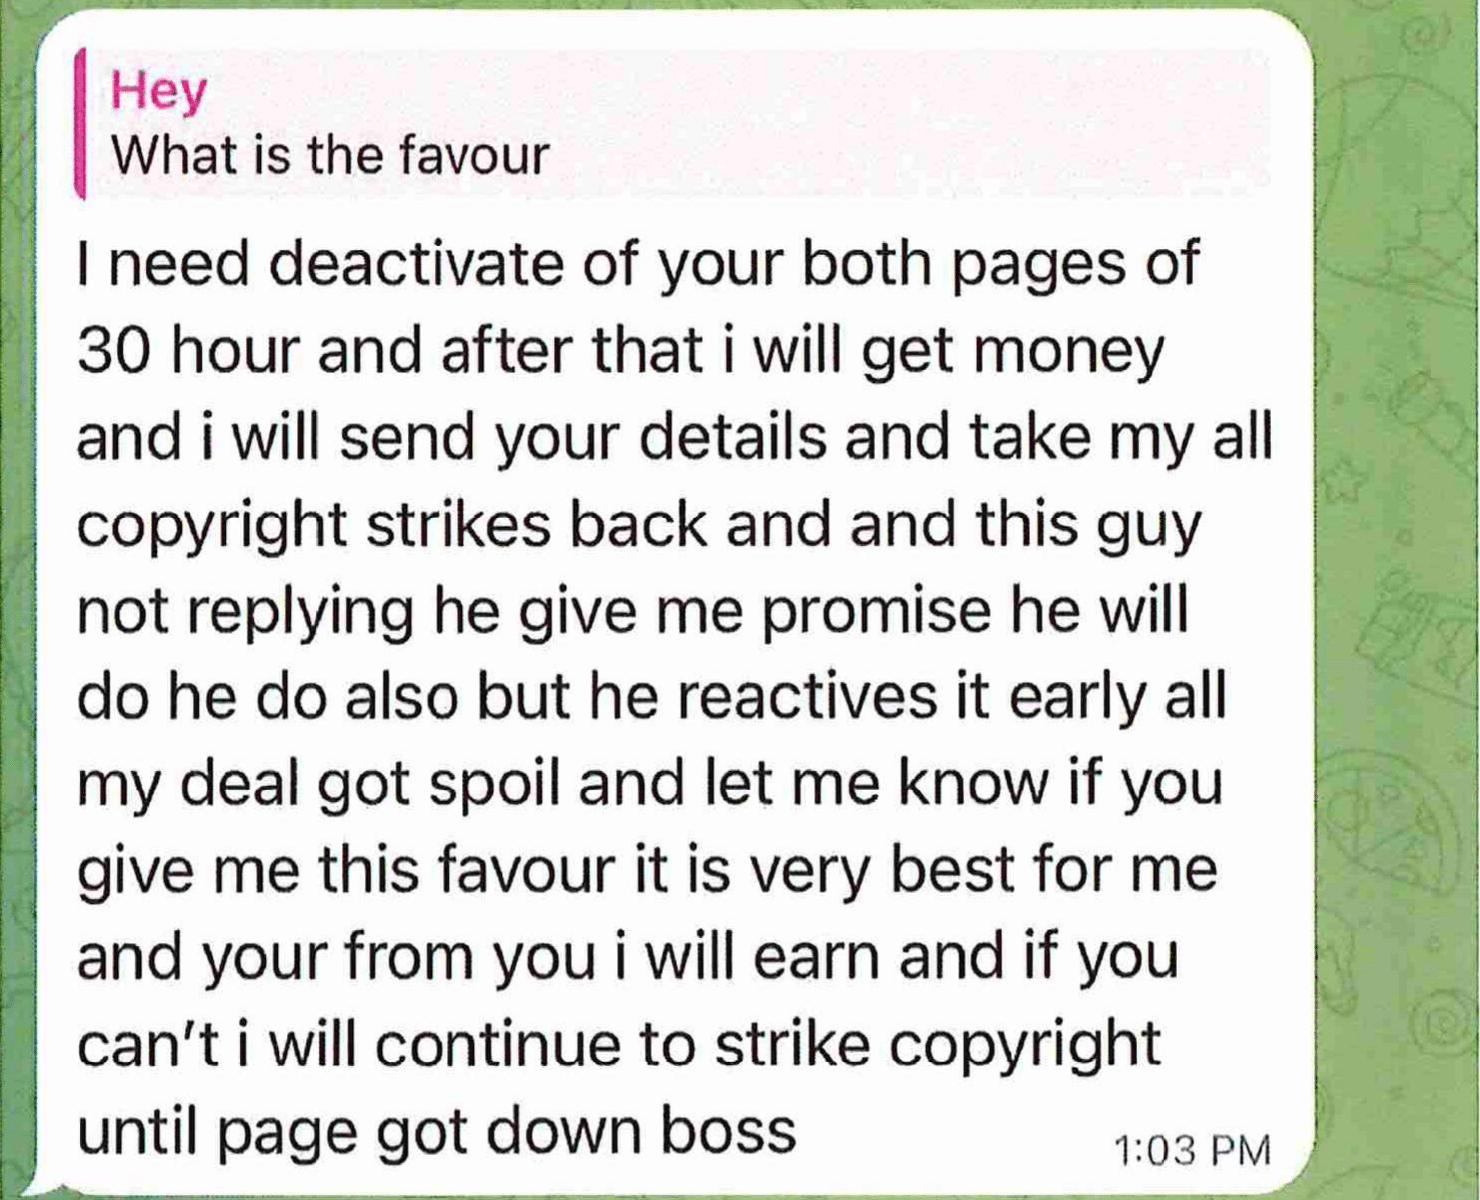
    The conversation then moved to Telegram, where the contractor uses the handle “Fix My Brand.” His good plan required The Dog Book to take its own social media accounts offline.

    The good plan

    The good plan

    In other words, if The Dog Book went dark for 30 hours, the contractor could collect the money from his client and then withdraw the strikes.

    Playing Along

    According to its own messages, The Dog Book played along at least once and took its pages offline during a weekend. That didn’t go as planned, however, as the contractor complained that the pages came back too soon. As a result, he didn’t get paid by his client.

    “You do 18 hour i dont get my payment. Okay if you are not in a mood boss no issue. I will take down your ig now when you get in your mood let me know after your ig burn,” he wrote.

    The bookseller, meanwhile, wanted names of those who requested the takedowns. When it listed Remus and its principals, the contractor answered “Yes.” Later, he wrote that if his clients found out, “they will cancle all my deals.”

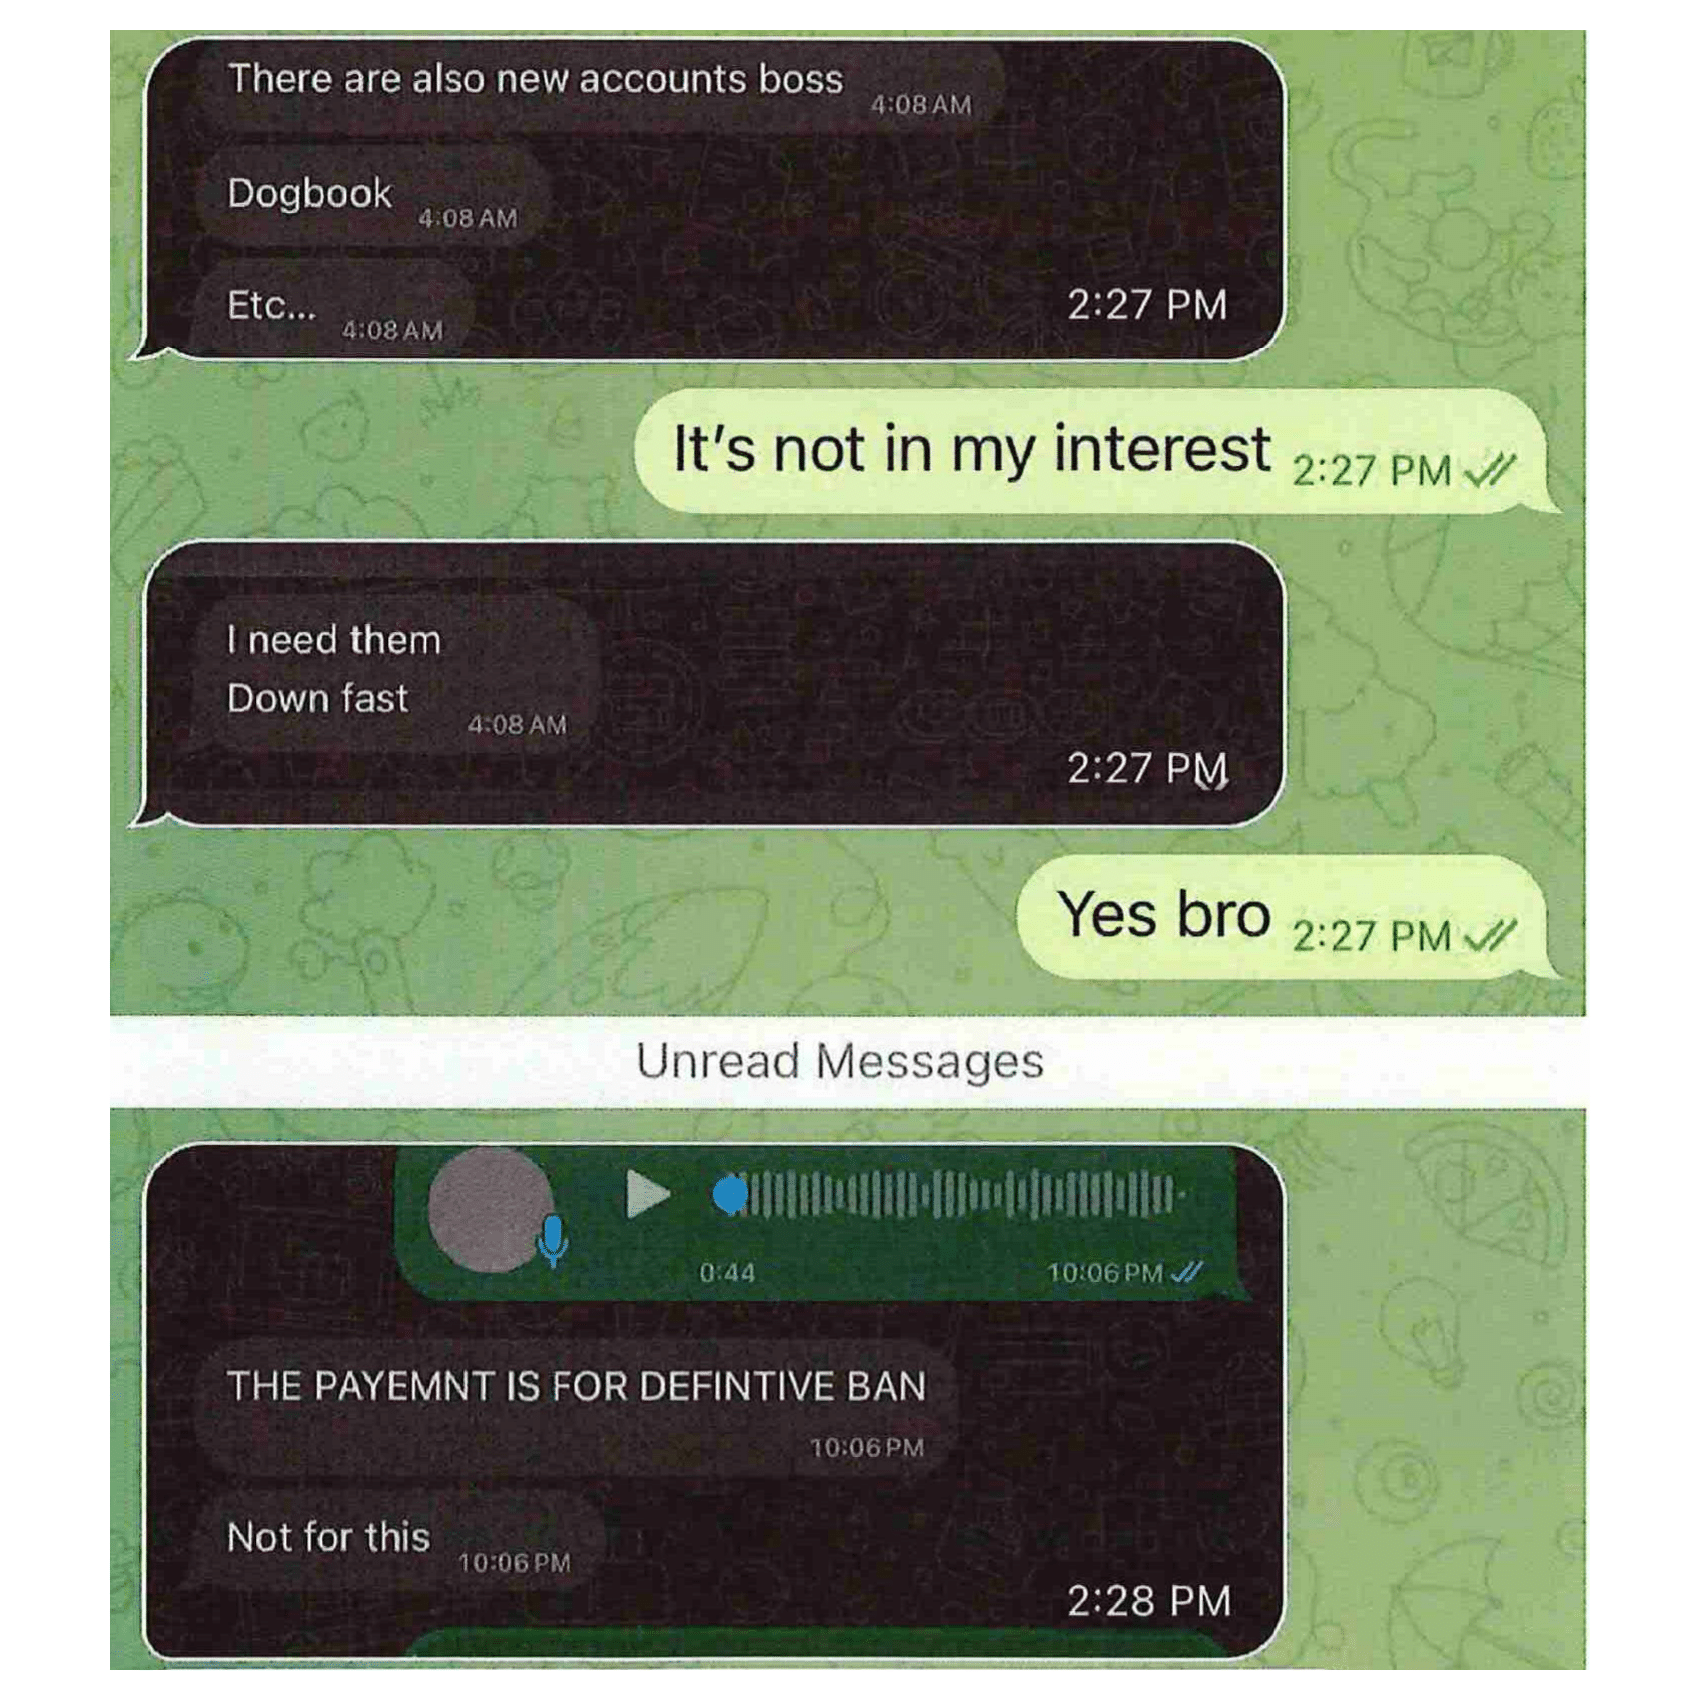
    To back up his story, he forwarded messages from the person who, according to the complaint, was directing the takedown spree. One of these messages clearly states what the payment was for.

    Forwarded messages

    Forwarded messages

    “THE PAYEMNT IS FOR DEFINTIVE BAN,” it reads.

    Still in Business

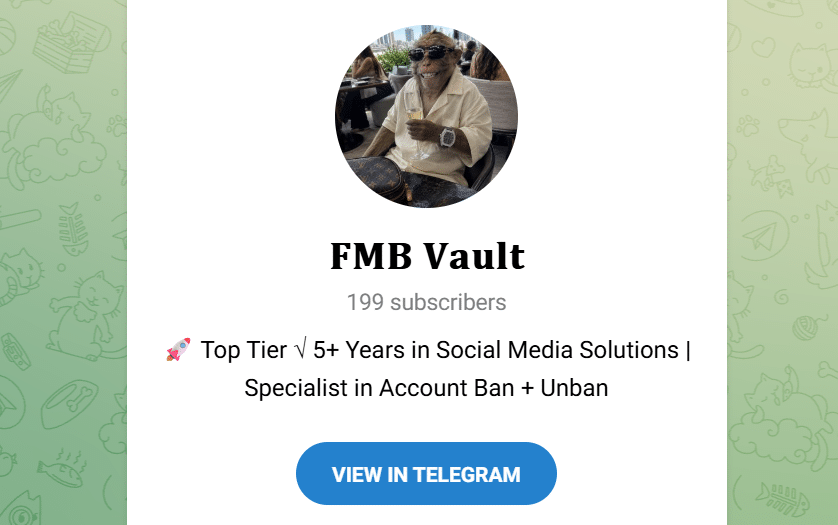
    According to the complaint, “Fix My Brand” is a commercial vendor selling account suspensions, who also runs the Telegram channel “FMB Vault.” This channel is still online at the time of writing, with 199 subscribers and a biography that now describes the operator as a “Specialist in Account Ban + Unban.”

    FMB Vault’s Telegram

    FMB Vault

    Meanwhile, The Dog Book says the campaign continues. According to the complaint, its Facebook accounts were reported more than four hundred times in recent weeks, with someone claiming that they showed sexually explicit content.

    “Plaintiff’s accounts contain no sexually explicit content of any kind, and never have. Plaintiff’s accounts display photographs of dogs and of photographic books about dogs, together with product information and ordinary commercial marketing copy,” the complaint clarifies.

    The Dog Book accuses the defendants of DMCA misrepresentation, false advertising and defamation, among other claims, and puts its losses at more than $600,000.

    None of these allegations have been tested in court, and the defendants have yet to appear in the case.

    False copyright claims and blackmail schemes on social media are nothing new. However, as far as we know, this is the first U.S. lawsuit that targets a vendor who allegedly sells takedowns and suspensions as a service.

    —

    A copy of The Dog Book’s complaint is available here (pdf). The exhibits with the copyright notices, Telegram messages and Instagram stories can be found here (pdf).

    From: TF, for the latest news on copyright battles, piracy and more.

    • chevron_right

      Nintendo Targets Picofly Switch Modchip Firmware in GitHub DMCA Takedown

      news.movim.eu / TorrentFreak • 11 November 2026 • 3 minutes

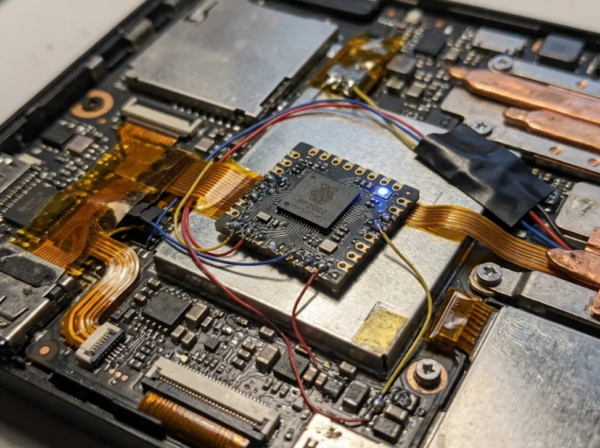
    picoflyIn 2020, Nintendo went to court to stop the sale of SX Core and SX Lite, two Team-Xecuter modchips designed to work on all Switch consoles at the time.

    These lawsuits were followed by a criminal prosecution in the United States, and Team-Xecuter’s operation effectively shut down. The chips lived on, however, and remained available through compatible alternatives such as HWFLY and Picofly.

    Now, Nintendo is also going after the repositories that host the firmware for these modchips.

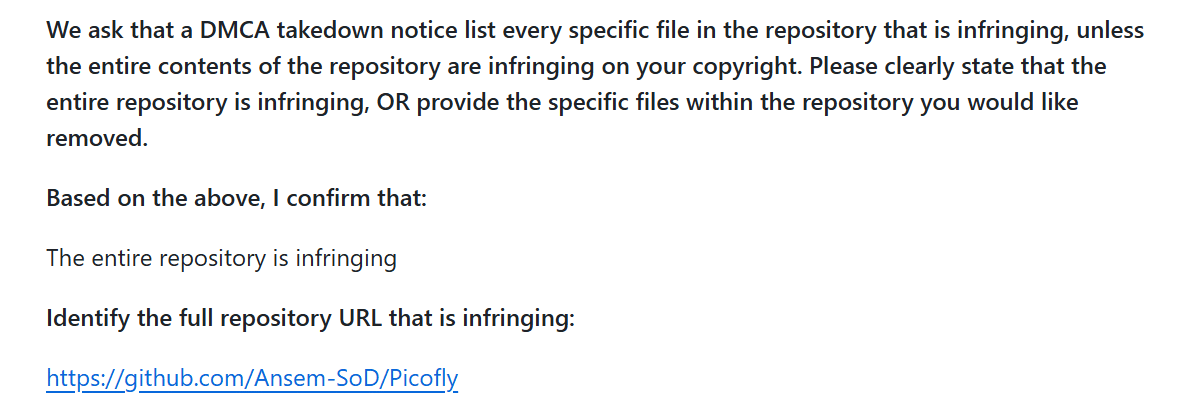
    In a takedown notice dated November 6, which GitHub published on Tuesday, Nintendo of America targets Ansem-SoD/Picofly. According to its description, this repository offered information and firmware for a Switch modchip based on the RP2040-Zero board.

    Picofly

    picofly notice

    The notice names only the parent repository, but its effect doesn’t stop there. Because the network was larger than a hundred repos and Nintendo said that all or most forks are infringing, GitHub disabled the entire network of 144 repositories.

    From Emulators to Modchips

    Nintendo’s earlier GitHub notices mostly went after emulators, key dumping tools and so-called sigpatches. This time, the gaming giant targets repositories offering firmware for SX Core, SX Lite, Picofly and HWFLY modchips.

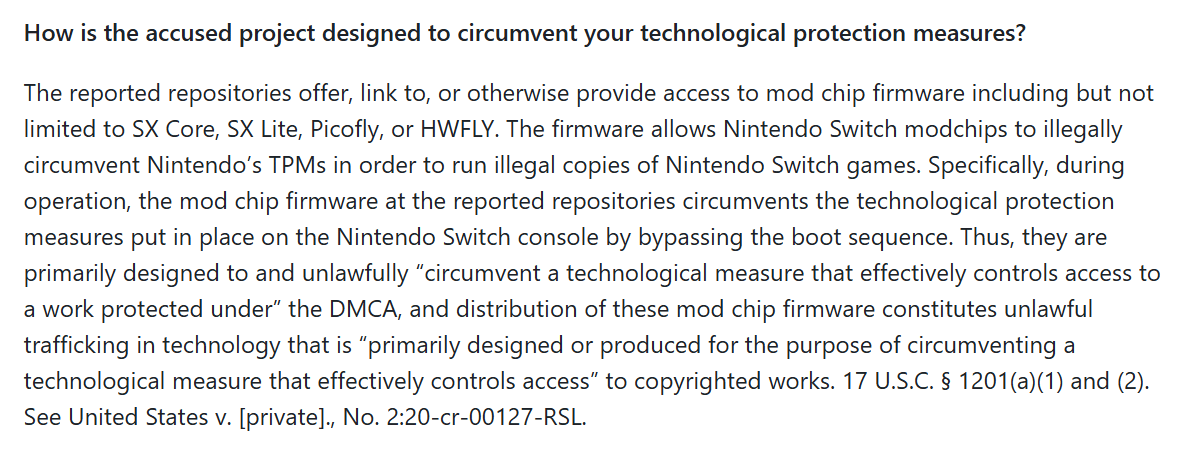
    According to Nintendo, the Switch’s technological protection measures (TPMs) include the console’s boot sequence and various cryptographic signatures. The company says the modchip firmware bypasses that boot sequence, violating the DMCA’s anti-circumvention provisions.

    “The firmware allows Nintendo Switch modchips to illegally circumvent Nintendo’s TPMs in order to run illegal copies of Nintendo Switch games,” the notice reads.

    From Nintendo’s notice

    From Nintendo's notice

    As far as we know, this is the first time Nintendo has targeted modchip firmware on GitHub. None of the 90 earlier Nintendo notices in GitHub’s public archive mention modchips. The closest are the 2023 and 2024 notices against key dumping tools such as Lockpick_RCM.

    A Team-Xecuter Precedent

    To support its circumvention claim, the notice points to the criminal case No. 2:20-cr-00127-RSL. That’s the case against the alleged members of Team-Xecuter.

    The U.S. indicted three people in 2020. One of them, Gary Bowser, pleaded guilty to conspiring to circumvent technological measures and to traffic in circumvention devices. He was later sentenced to 40 months in prison.

    The other two defendants, including alleged leader Max Louarn, have not appeared before the U.S. court as far as we know, and both remain at large.

    It’s worth noting that Bowser’s guilty plea is not a court ruling on modchip firmware. However, at the takedown stage, Nintendo doesn’t need one, and GitHub appears to have processed the notice regardless.

    Firmware Still Online

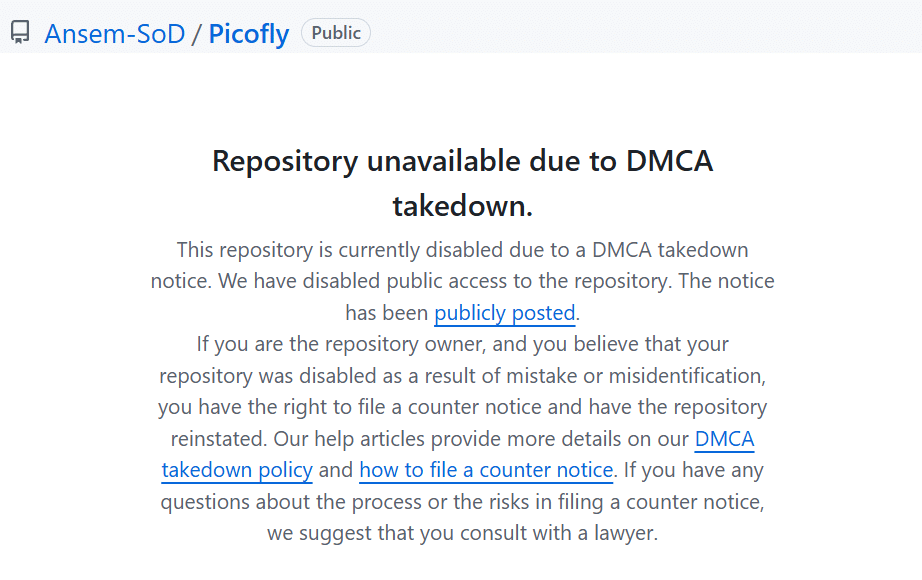
    When we checked on Wednesday, the Picofly repository was replaced by GitHub’s standard takedown message, which also explains that the owner can file a counter notice.

    Repository unavailable

    However, not all modchip firmware is gone. Several other GitHub repositories with Picofly and HWFLY firmware were still online, including what a GBAtemp forum user describes as the original Picofly source. None of these are named in Nintendo’s notice.

    Nintendo also sent three emulator notices on the same day. One targets the Citron Neo emulator, where GitHub disabled a network of 71 repositories, and two target single copies of yuzu.

    Nintendo’s November 6 notices (published later)
    Repository Project Repos Status
    Ansem-SoD/Picofly Picofly firmware 144 Disabled
    citron-neo/emulator Citron Neo 71 Forks disabled
    IpwnedU/yuzu-mainline-master yuzu 1 Code removed
    IpwnedU/yuzu-android-master yuzu 1 Code removed

    These yuzu repositories are still on GitHub, but their owner has since removed the code and cleared the commit history. Both now only host a README which says that the source code can be found on the Internet Archive.

    For now, the Picofly network remains offline. Its owner can still file a counter notice, but GitHub’s archive shows no sign of one yet.

    —

    Nintendo’s DMCA notice targeting the Picofly repository is available at GitHub here. The Citron Neo notice can be found here, and the two yuzu notices here and here.

    From: TF, for the latest news on copyright battles, piracy and more.

    • chevron_right

      Pirate Library WeLib Hit With $19.5m Default Judgment and Domain Takedown Order

      news.movim.eu / TorrentFreak • 10 November 2026 • 3 minutes

    welib logoIn June, WeLib became the second shadow library to be sued by the same group of book companies, after Anna’s Archive.
    According to the complaint, the relatively young site was built on code and books that it copied from Anna’s Archive.

    WeLib’s anonymous operators didn’t respond to the lawsuit, which prompted the publishers to request a default judgment last month. Their brief borrowed heavily from one they had filed against Anna’s Archive earlier this year, including a claim about BitTorrent that didn’t appear to fit the WeLib case.

    After reviewing the paperwork, U.S. District Judge Victor Marrero nonetheless granted the request in full. In an order issued yesterday, he gave the publishers everything they asked for.

    Maximum Damages

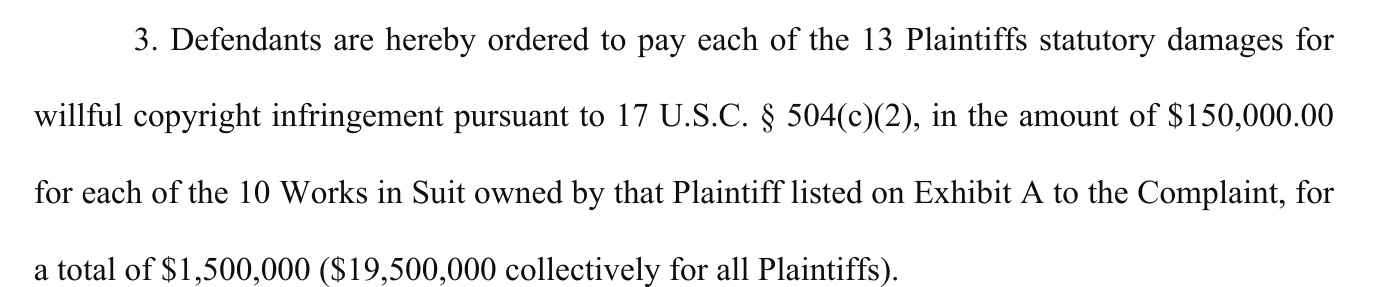
    The judgment awards each of the thirteen publishers, which include Penguin Random House, Elsevier and HarperCollins, $150,000 per book for ten of their works listed in the complaint. That is the maximum in statutory damages for willful infringement, adding up to $1.5 million per publisher.

    $19.5 million

    $19.5 million

    The total of $19.5 million matches what Judge Jed Rakoff awarded against Anna’s Archive in May. While that is a big win, collecting it is another matter, as WeLib’s operators have not been identified.

    The judgment does order the WeLib operators to come forward. In addition to destroying all unauthorized copies of the publishers’ works, they must file a sworn report within ten business days after being served, including valid contact information for WeLib and “each of its managing agents.”

    Domain Takedowns

    The judgment also includes a permanent injunction that prevents WeLib from making the publishers’ works available anywhere in the world. At the same time, it targets the infrastructure that keeps the site online.

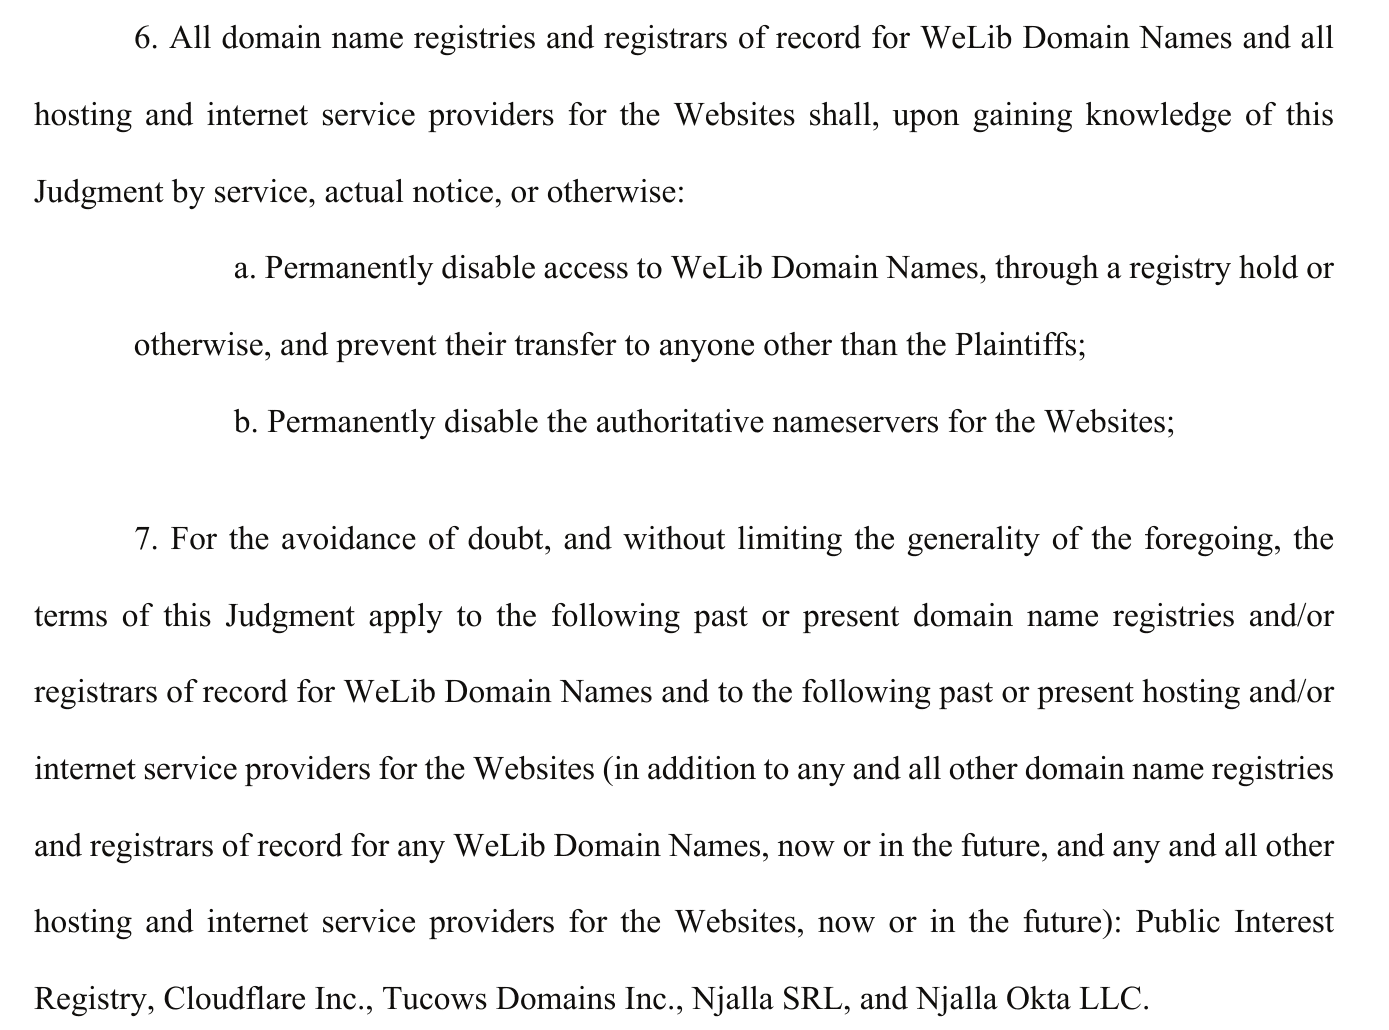
    All domain name registries, registrars and hosting providers for the site are ordered to permanently disable welib.org, welib.st and welib-public.org. They also have to disable the site’s nameservers and stop hosting it, while preserving any evidence that could identify the operators.

    Domains and intermediaries

    Domains and intermediaries

    The order names five past or present providers specifically: Public Interest Registry, Cloudflare, Tucows and two Njalla entities. That said, it also applies to all other registries, registrars and hosting providers for WeLib’s domains, now or in the future.

    Signed Word for Word

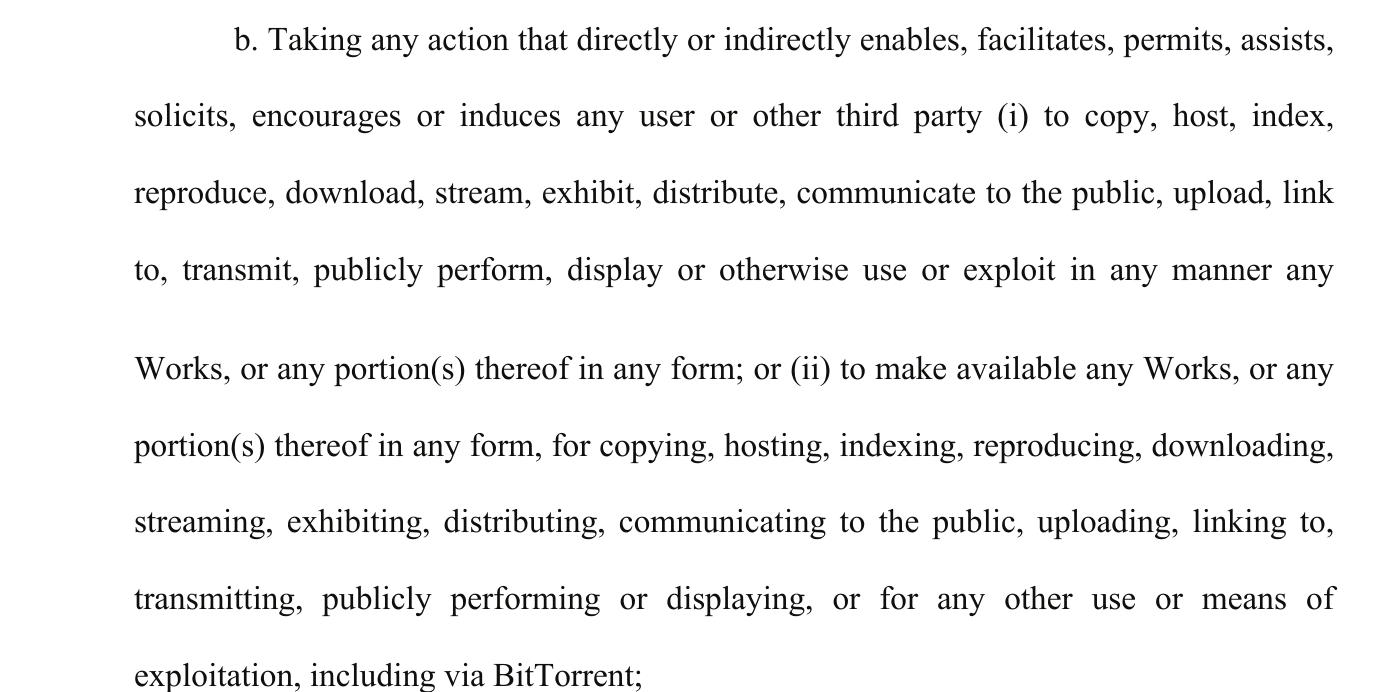
    The judgment is identical to the proposed order the publishers submitted in October and Judge Marrero signed it without changes. That includes the clause preventing WeLib from enabling users or third parties to make the works available, “including via BitTorrent.”

    Including via BitTorrent

    Including via BitTorrent

    As far as we know, there is no evidence that WeLib uses BitTorrent. The WeLib complaint doesn’t mention it either. The same clause appears in the earlier default judgment against Anna’s Archive, where the complaint described the site’s dedicated “Torrents” page.

    Still Online

    With the injunction in hand, the publishers will likely ask intermediaries to take action. This includes the Public Interest Registry, which manages the .org domain and is based in the United States. Foreign intermediaries may not all comply with an American court order, however.

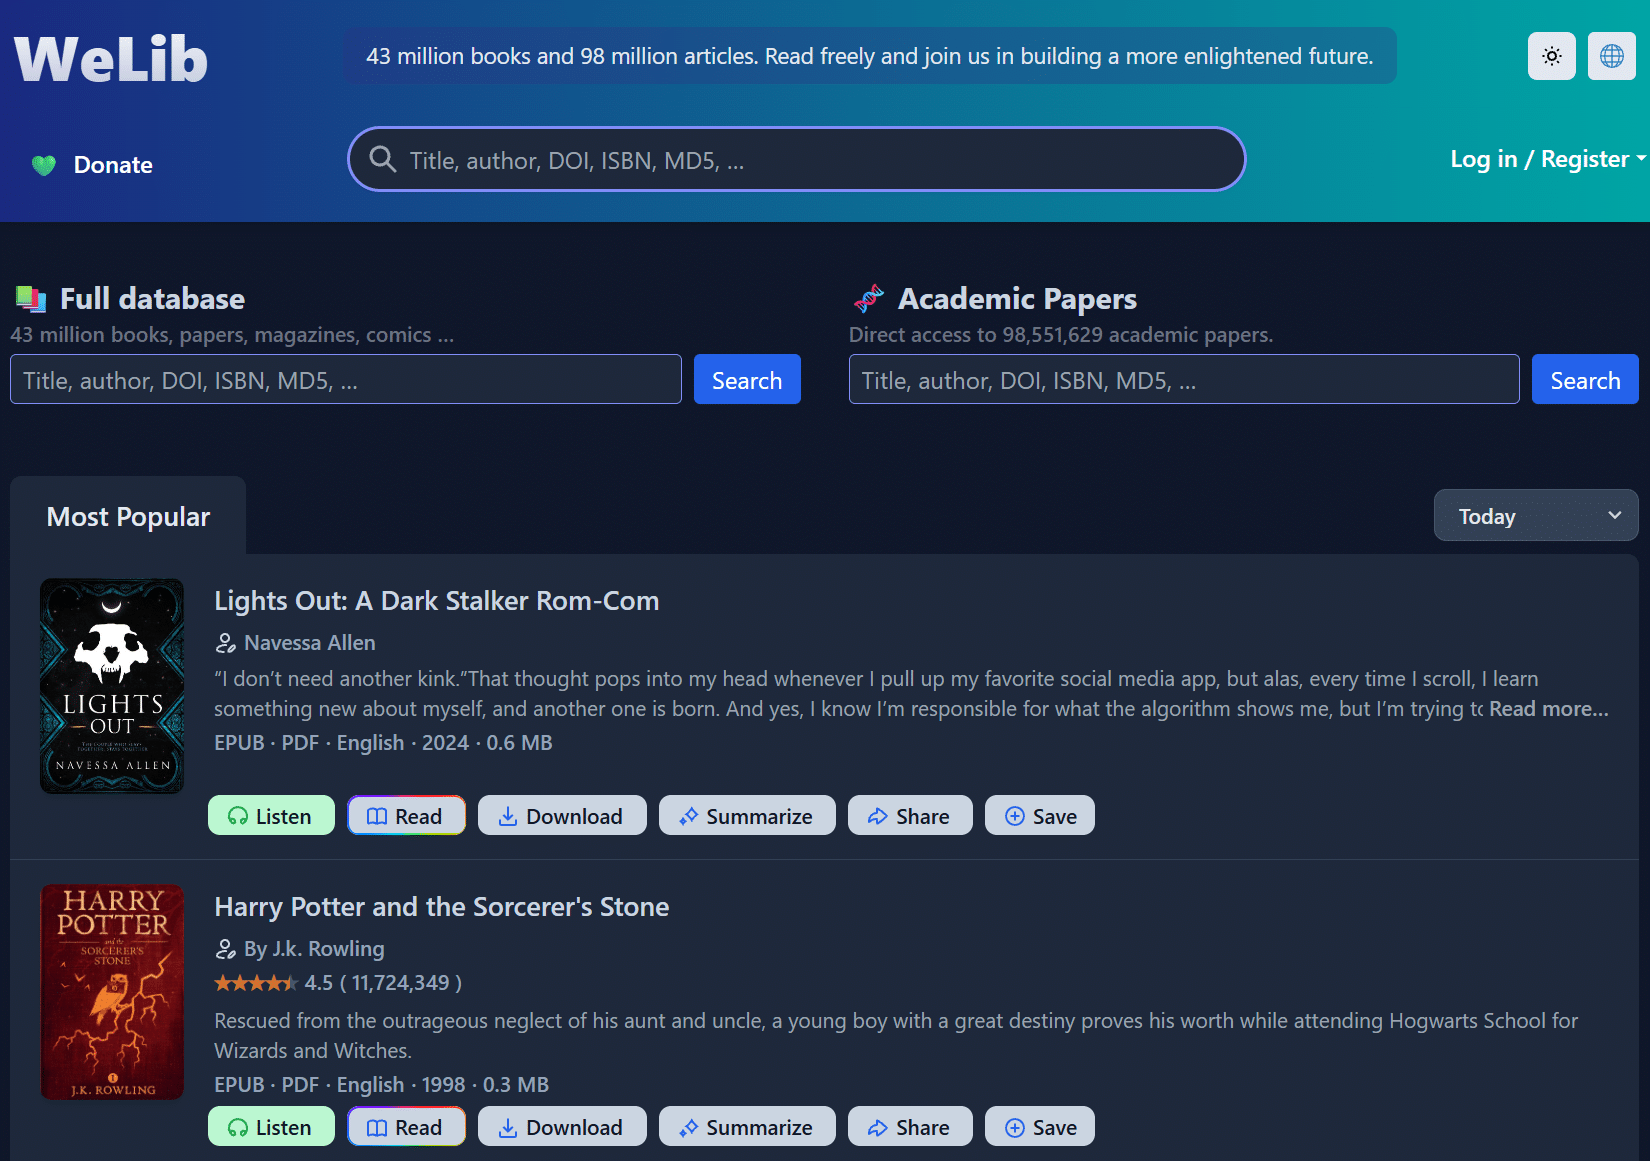
    At the time of writing, welib.org and welib.st still load the familiar search page, advertising 43 million books and 98 million articles.

    WeLib, still online

    welib

    Anna’s Archive also lost several domains to an earlier injunction, obtained by music companies. However, it remains online through .gl, .pk and .gd domains, which are tied to registries and registrars outside the United States.

    Whether WeLib plans to copy the moves of Anna’s Archive has yet to be seen, but given its history that would not be a surprise.

    —

    A copy of the default judgment, signed by Judge Victor Marrero on November 9, 2026, is available here (pdf). The publishers’ proposed order can be found here (pdf).

    From: TF, for the latest news on copyright battles, piracy and more.

    • chevron_right

      Movistar Blocks Its Own Support Forum Under LaLiga Anti-Piracy Order

      news.movim.eu / TorrentFreak • 9 November 2026 • 2 minutes

    movistar blockEvery LaLiga match weekend, Spanish Internet providers must block hundreds of IP addresses that are linked to pirate football streams.

    These blocks are the result of a December 2024 court order, obtained by LaLiga and Telefónica Audiovisual Digital, which broadcasts these matches on Movistar Plus+. The order targets Spain’s largest ISPs, including Telefónica’s own.

    LaLiga is pleased with the blocking measures and said that they work as intended. However, they are not without controversy, as IP address blocks previously hit broader infrastructure including shared Cloudflare servers. On Saturday, this collateral damage landed in Telefónica’s own backyard.

    Movistar Blocks Movistar

    On Saturday evening, Movistar’s official forum became unreachable through several Spanish ISPs.

    This Comunidad Movistar forum is where the ISP’s customers go for help with their routers, Movistar Plus+ programming, or to report outages. Shortly after 22:00, this support community became unreachable.

    According to RedesZone, X user Alvaro Canteiro was the first to notice. At 22:17, he posted that LaLiga appeared to have blocked Movistar’s official forum, presumably as a side effect of its anti-piracy blocking.

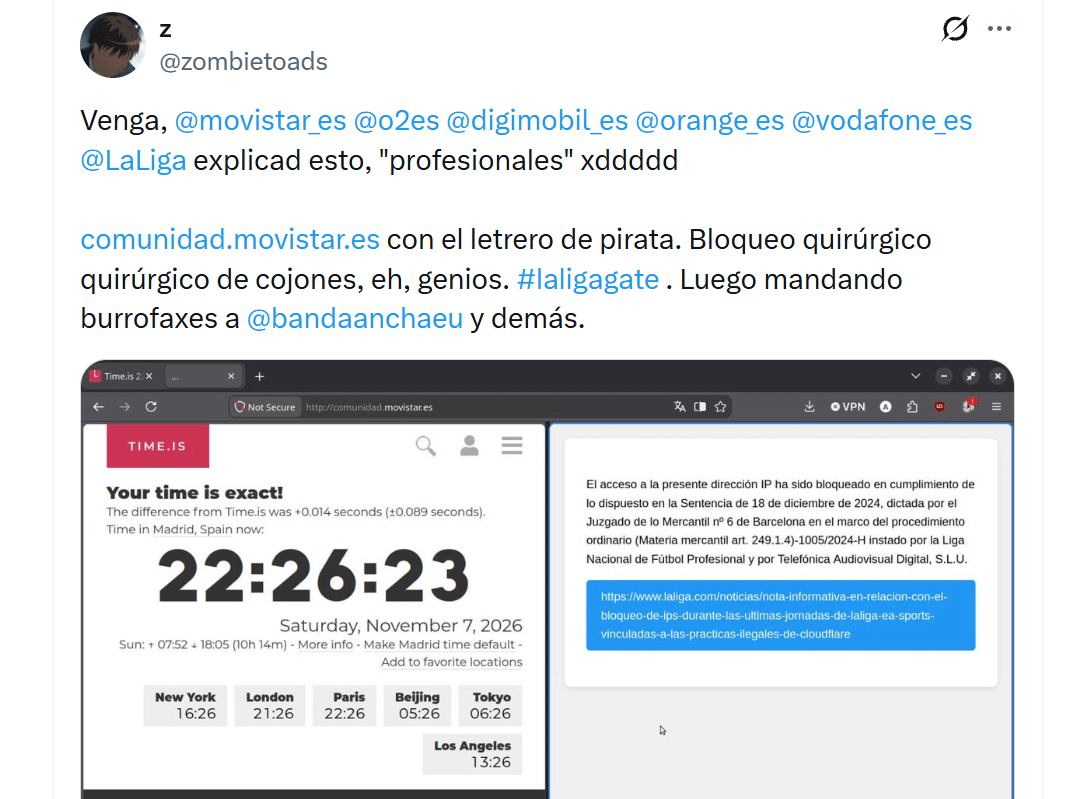
    Those who tried to visit the forum through rival ISP DIGI saw a blocking notice. It explained that the IP address was blocked under the December 18, 2024 ruling of the Commercial Court No. 6 in Barcelona, requested by LaLiga and Telefónica Audiovisual Digital.

    Blocked (via @zombietoads)

    Blocked

    DIGI wasn’t alone. Bandaancha reports that Telefónica routed the forum’s IP address into a black hole, leaving visitors in the dark, without any response at all.

    Based on data from blocking tracker HayAhoraFútbol, RedesZone reports that all operators blocked the two Cloudflare IP addresses the forum used at the time. That included Movistar, which effectively blocked access to its own community.

    Blocked Cloudflare IP addresses are nothing new in Spain. LaLiga started targeting them in February 2025, and site owners have complained about collateral damage on match days ever since.

    ‘Focused, Precise’

    Under the court order, LaLiga identifies IP addresses that it associates with pirate streams, which ISPs are then required to block. This order is dynamic, allowing LaLiga and Telefónica to add new successor IP addresses based on their own assessment.

    These blocks typically start shortly before a match starts and are removed again after the broadcast ends.

    Why the forum’s IP addresses ended up on the blocklist is unknown. Neither LaLiga nor Movistar has confirmed the cause of the outage.

    LaLiga has consistently defended this blocking approach. The league previously told TorrentFreak that its blocks are backed by judicial resolutions and are not indiscriminate. Third parties who believe they are affected can report this through a dedicated complaints mailbox, LaLiga clarified.

    Forum Moves to CloudFront

    By Sunday, the forum had moved to a different CDN. Both Bandaancha and RedesZone noticed that the domain no longer pointed to Cloudflare, but was linked to Amazon’s CloudFront instead.

    A DNS lookup by TorrentFreak today shows that comunidad.movistar.es now points to movistar.lithium.com, which is indeed served through CloudFront. Who made the switch, and whether it was a direct response to the blocking, is not known.

    Whether affected Movistar users will complain about the apparent overblocking has yet to be seen.

    Last year, LaLiga told TorrentFreak that it hadn’t received any formal complaints, while stressing that the blocking system was “focused, precise, and without collateral impact on legitimate services.”

    From: TF, for the latest news on copyright battles, piracy and more.